

ITP with Entra ID (legacy)
Set up the legacy Entra ID connector for CrowdStrike ITP by creating an application in Entra ID. This connector is deprecated and only available in specific cases, on request to Stoïk: use the current setup instead.
Prerequisites
A paid Entra ID license. Microsoft Entra ID Free is not supported.
An account with global administrator rights to your Entra ID account.
Purpose of ITP
The ITP (Identity Threat Protection) option continuously monitors account-related activities and Active Directory to detect abnormal behavior.
Identity-centered behavioral analysis
Suspicious authentications
Unusual access patterns
Unauthorized login attempts
User account anomalies
Examples of detected events: suspicious workstation-to-server connections, network scans, brute-force attempts, or credential extraction. When a critical event is identified, the module can automatically block it.
Assessment of your Active Directory security posture
The module provides a real-time overview of your Active Directory security, similar to the Stoïk Protect AD scan but with more advanced options:
Identification of configuration issues
Detection of accounts with compromised passwords
Management and control of user privileges
Cloud threat monitoring (optional)
When configured with your identity service (e.g. Entra ID), ITP can detect threats in your cloud environments:
Logins from suspicious IP addresses
Abnormal access attempts to user accounts
Integration
The integration requires the following steps for each Azure tenant.
Create and configure an application in Entra ID
In the Azure portal, open the left-hand menu and click
Microsoft Entra ID.From the
Addmenu, selectApp registrations.On the
Register an applicationpage:Under
Name, enter a name matching your internal conventions, or usestoik-connector-itp.Under
Supported account types, selectAccounts in this organizational directory only.Under
Redirect URI, selectWeband enterhttps://localhost.Click
Register.
In the application's left-hand menu, click
API permissions.Click
Add a permission.In the
Request API permissionspanel, clickMicrosoft Graph, then selectApplication permissions.In
Select permissions:Type
directory, expandDirectory, and selectDirectory.Read.All.Type
audit, expandAuditLog, and selectAuditLog.Read.All.
Click
Add permissions, then clickGrant admin consentand confirm.
Retrieve the application ID and secret
In Microsoft Entra ID, go to
App registrationsand select your application.In
Overview, note theApplication (client) ID.In
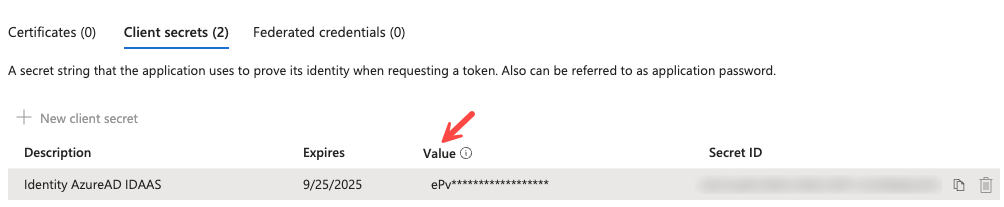
Certificates & secrets, create a new client secret: provide a description and an expiration duration.Save the generated value immediately. It will not be visible again.
Create a custom role for RBAC access
To display Azure RBAC role assignment information in Identity Protection, the application must be granted permission to read RBAC definitions and assignments.
Create the custom role
In the Azure portal, go to
Management Groups.Click
Tenant Root Group.Select
Access control (IAM), then clickRoles.Click
Add, then selectAdd custom role.In the
Basicstab, enter a clear name (e.g.Identity Protection RBAC Reader).In the
Permissionstab, add the following permissions:Click
Review + create, thenCreate.
Assign the custom role
In the Azure portal, go to
Management Groups.Click
Tenant Root Group.Select
Access control (IAM), then clickRole assignments.Click
Add, then selectAdd role assignment.In the
Roletab, select the custom role you just created.In the
Memberstab, clickSelect members, search for the previously created application (e.g.stoik-connector-itp), select it, and clickSelect.Click
Review + assign, thenReview + assignagain to confirm.
Transmit information to Stoïk
Send the following information to protect@stoik.io:
Tenant primary domain name (ends with
onmicrosoft.com)Application ID
Application secret
Without this information, the connector cannot be activated on our side.
Configure the connector in Identity Protection
In the Falcon console, go to
Identity Protection>Configure>Connectors.Select
Entraunder theIDAAScategory.Configure the connector with the tenant primary domain name, the application ID, and the application secret.
Enable the login data collection option.
Save the configuration.
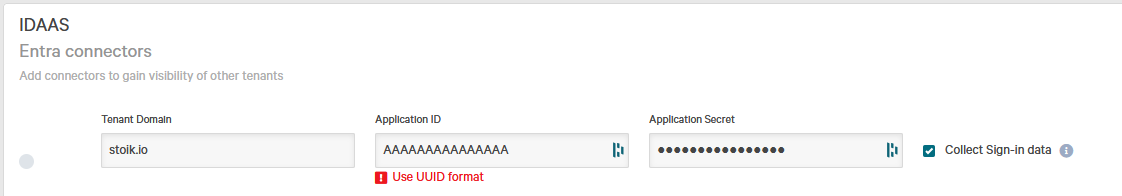
The status indicator turns green within a minute, confirming the connection has been successfully established.
Grant remediation access to Stoïk
If an account is compromised during nights or weekends, your teams may not be available to perform remediation. We recommend granting access so impacted accounts can be disabled once a compromise is confirmed.
Click the provided link, review the requested permissions, and click Accept. You will be redirected to a blank page, which you may close.
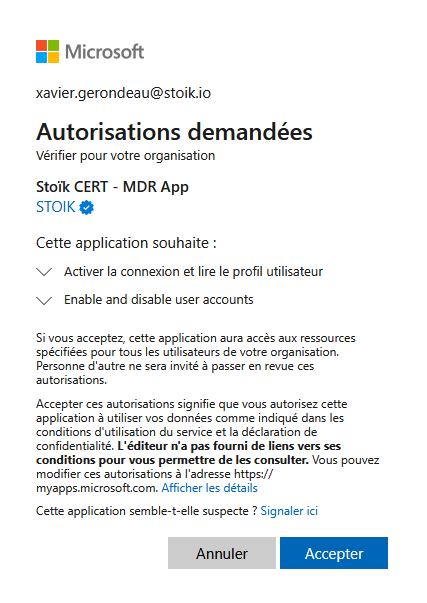
The application only has the permissions required to enable or disable existing accounts, with no ability to create accounts or modify other attributes. Each action is authenticated via MFA, logged, and timestamped. A complete audit log can be provided upon request.
Last updated