> For the complete documentation index, see [llms.txt](https://docs.stoik.io/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.stoik.io/prevention-tools/cloud-scan/entra-id.md).
# Setup: Entra ID
Give the Cloud scan read access to your Microsoft 365 tenant by assigning two reader roles to the Stoïk Cloud Scanner application.
## Prerequisites
* An Entra ID (Active Directory in the cloud) account with administrator access.
* A technical advisor is required for ongoing supervision and vulnerability remediation.
* One person does the whole setup, from start to finish: a Stoïk Protect user allowed to edit prevention tools, who is also an administrator of the Entra ID tenant.
* Signed in to a single Microsoft tenant: the one to scan. If the setup is stuck, restart it in a private browser window, signed in to that tenant only.
## Setup
{% stepper %}
{% step %}
### Select Entra ID
* If you haven't set a provider yet: go to `Cloud Scan` > `Launch Cloud Scan` > `Entra ID only`.
* If you already have a provider: go to `Cloud Scan` > `Settings` > `New Provider` > `Entra ID only`.
{% endstep %}
{% step %}
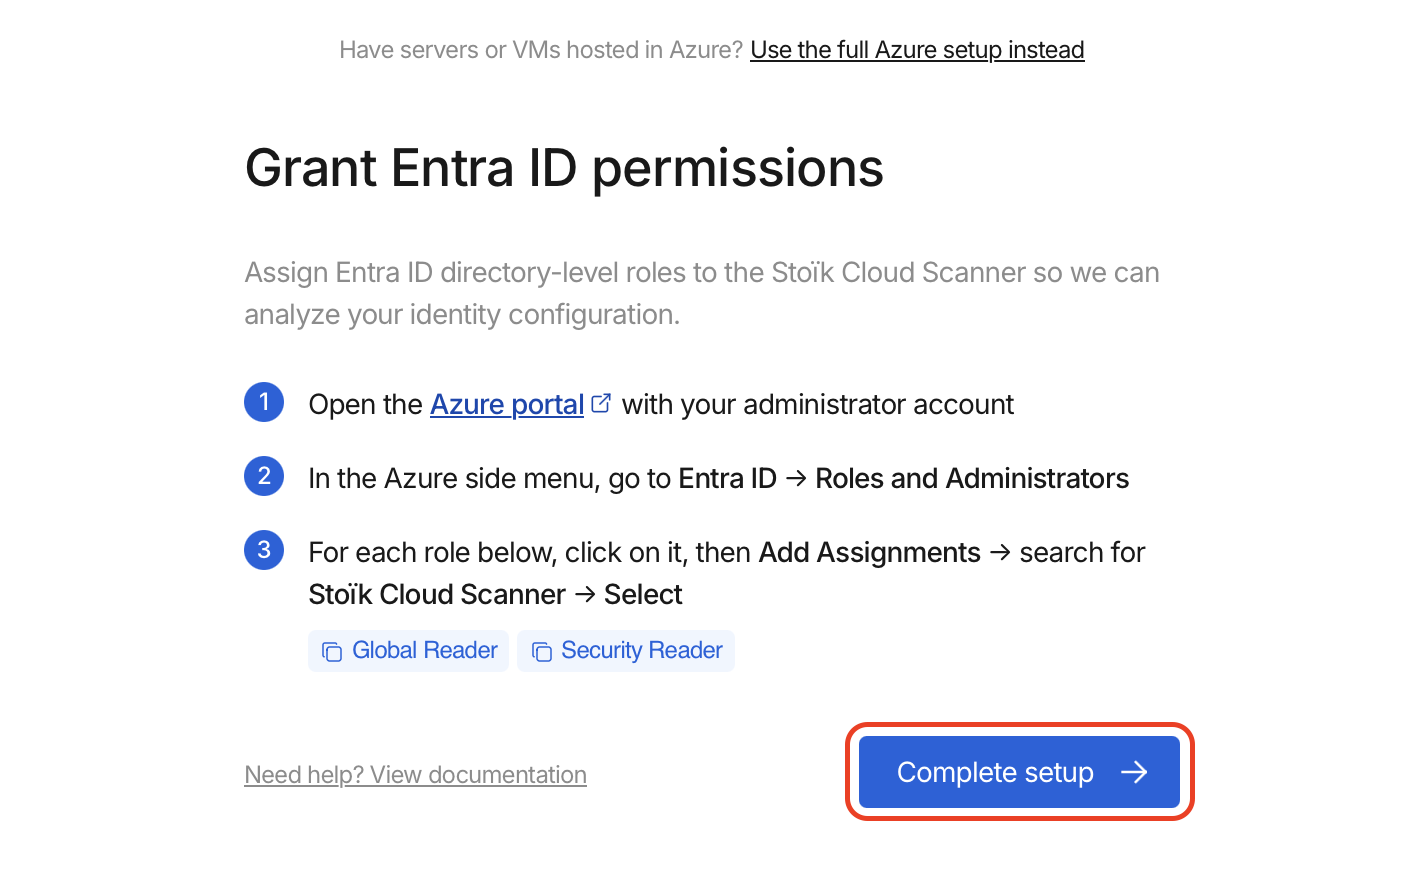
### Grant permissions
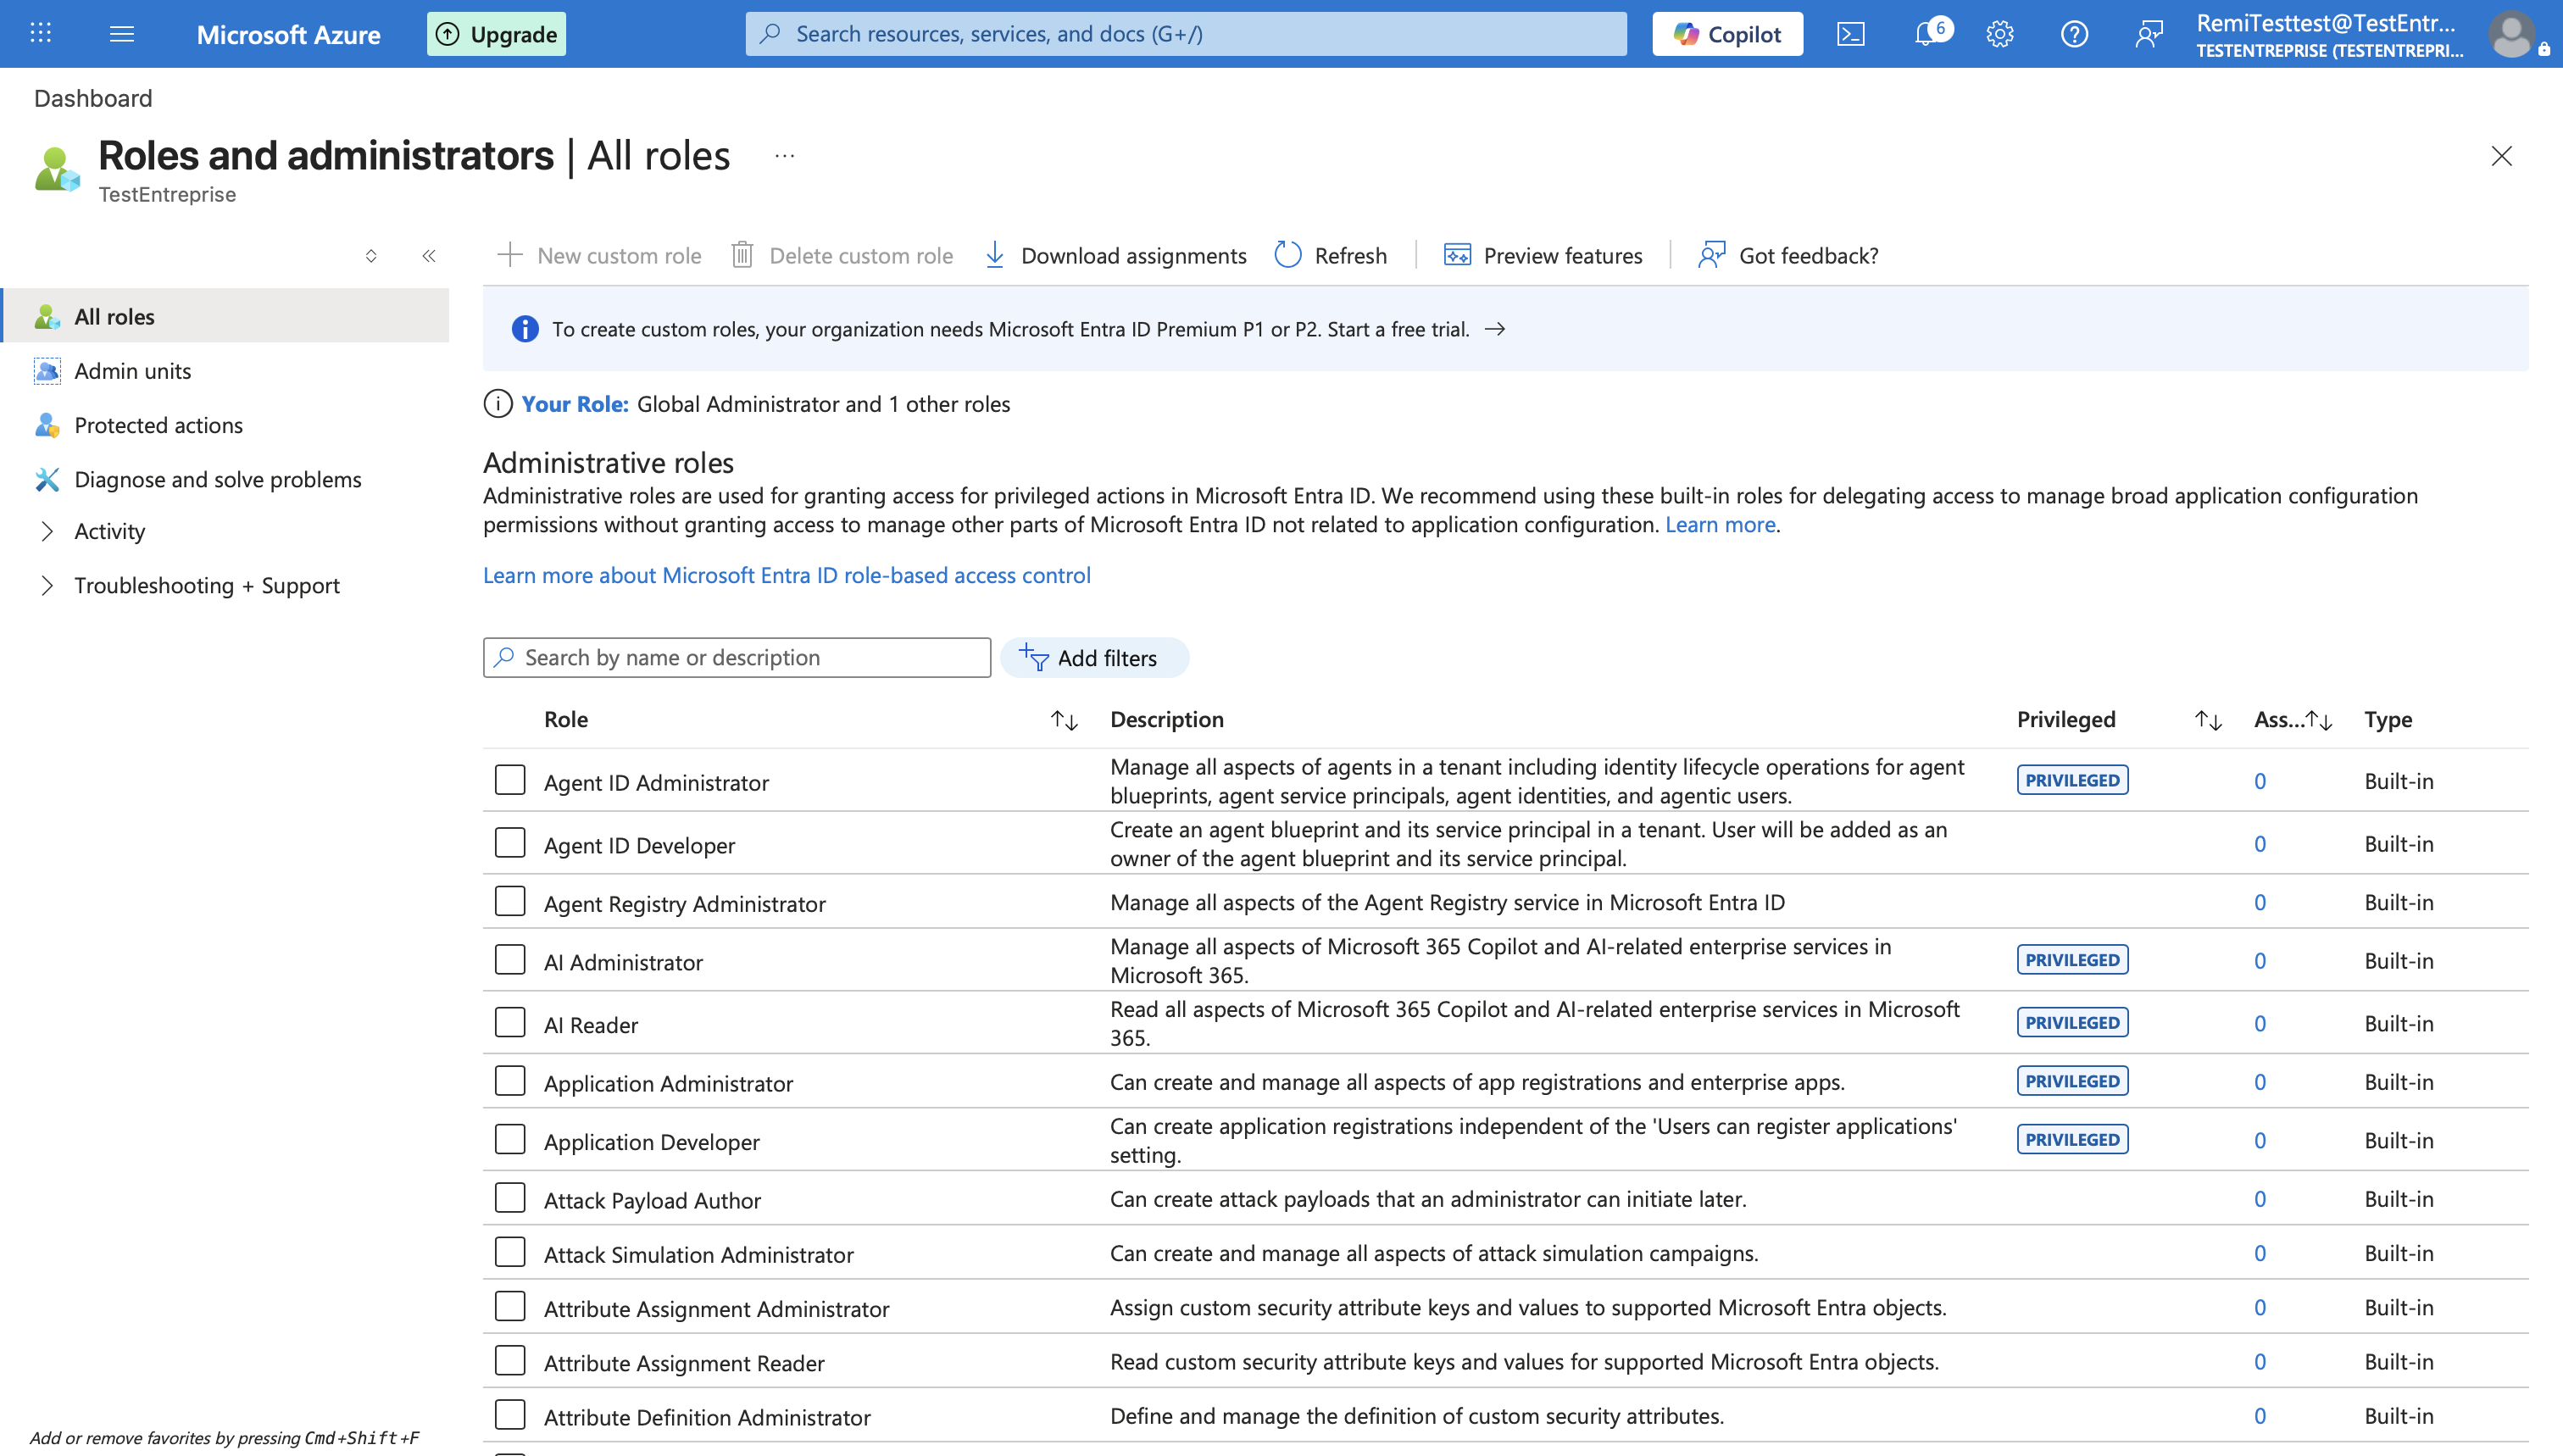
1. In the left-hand menu, go to `Microsoft Entra ID` > `Roles and administrators`.
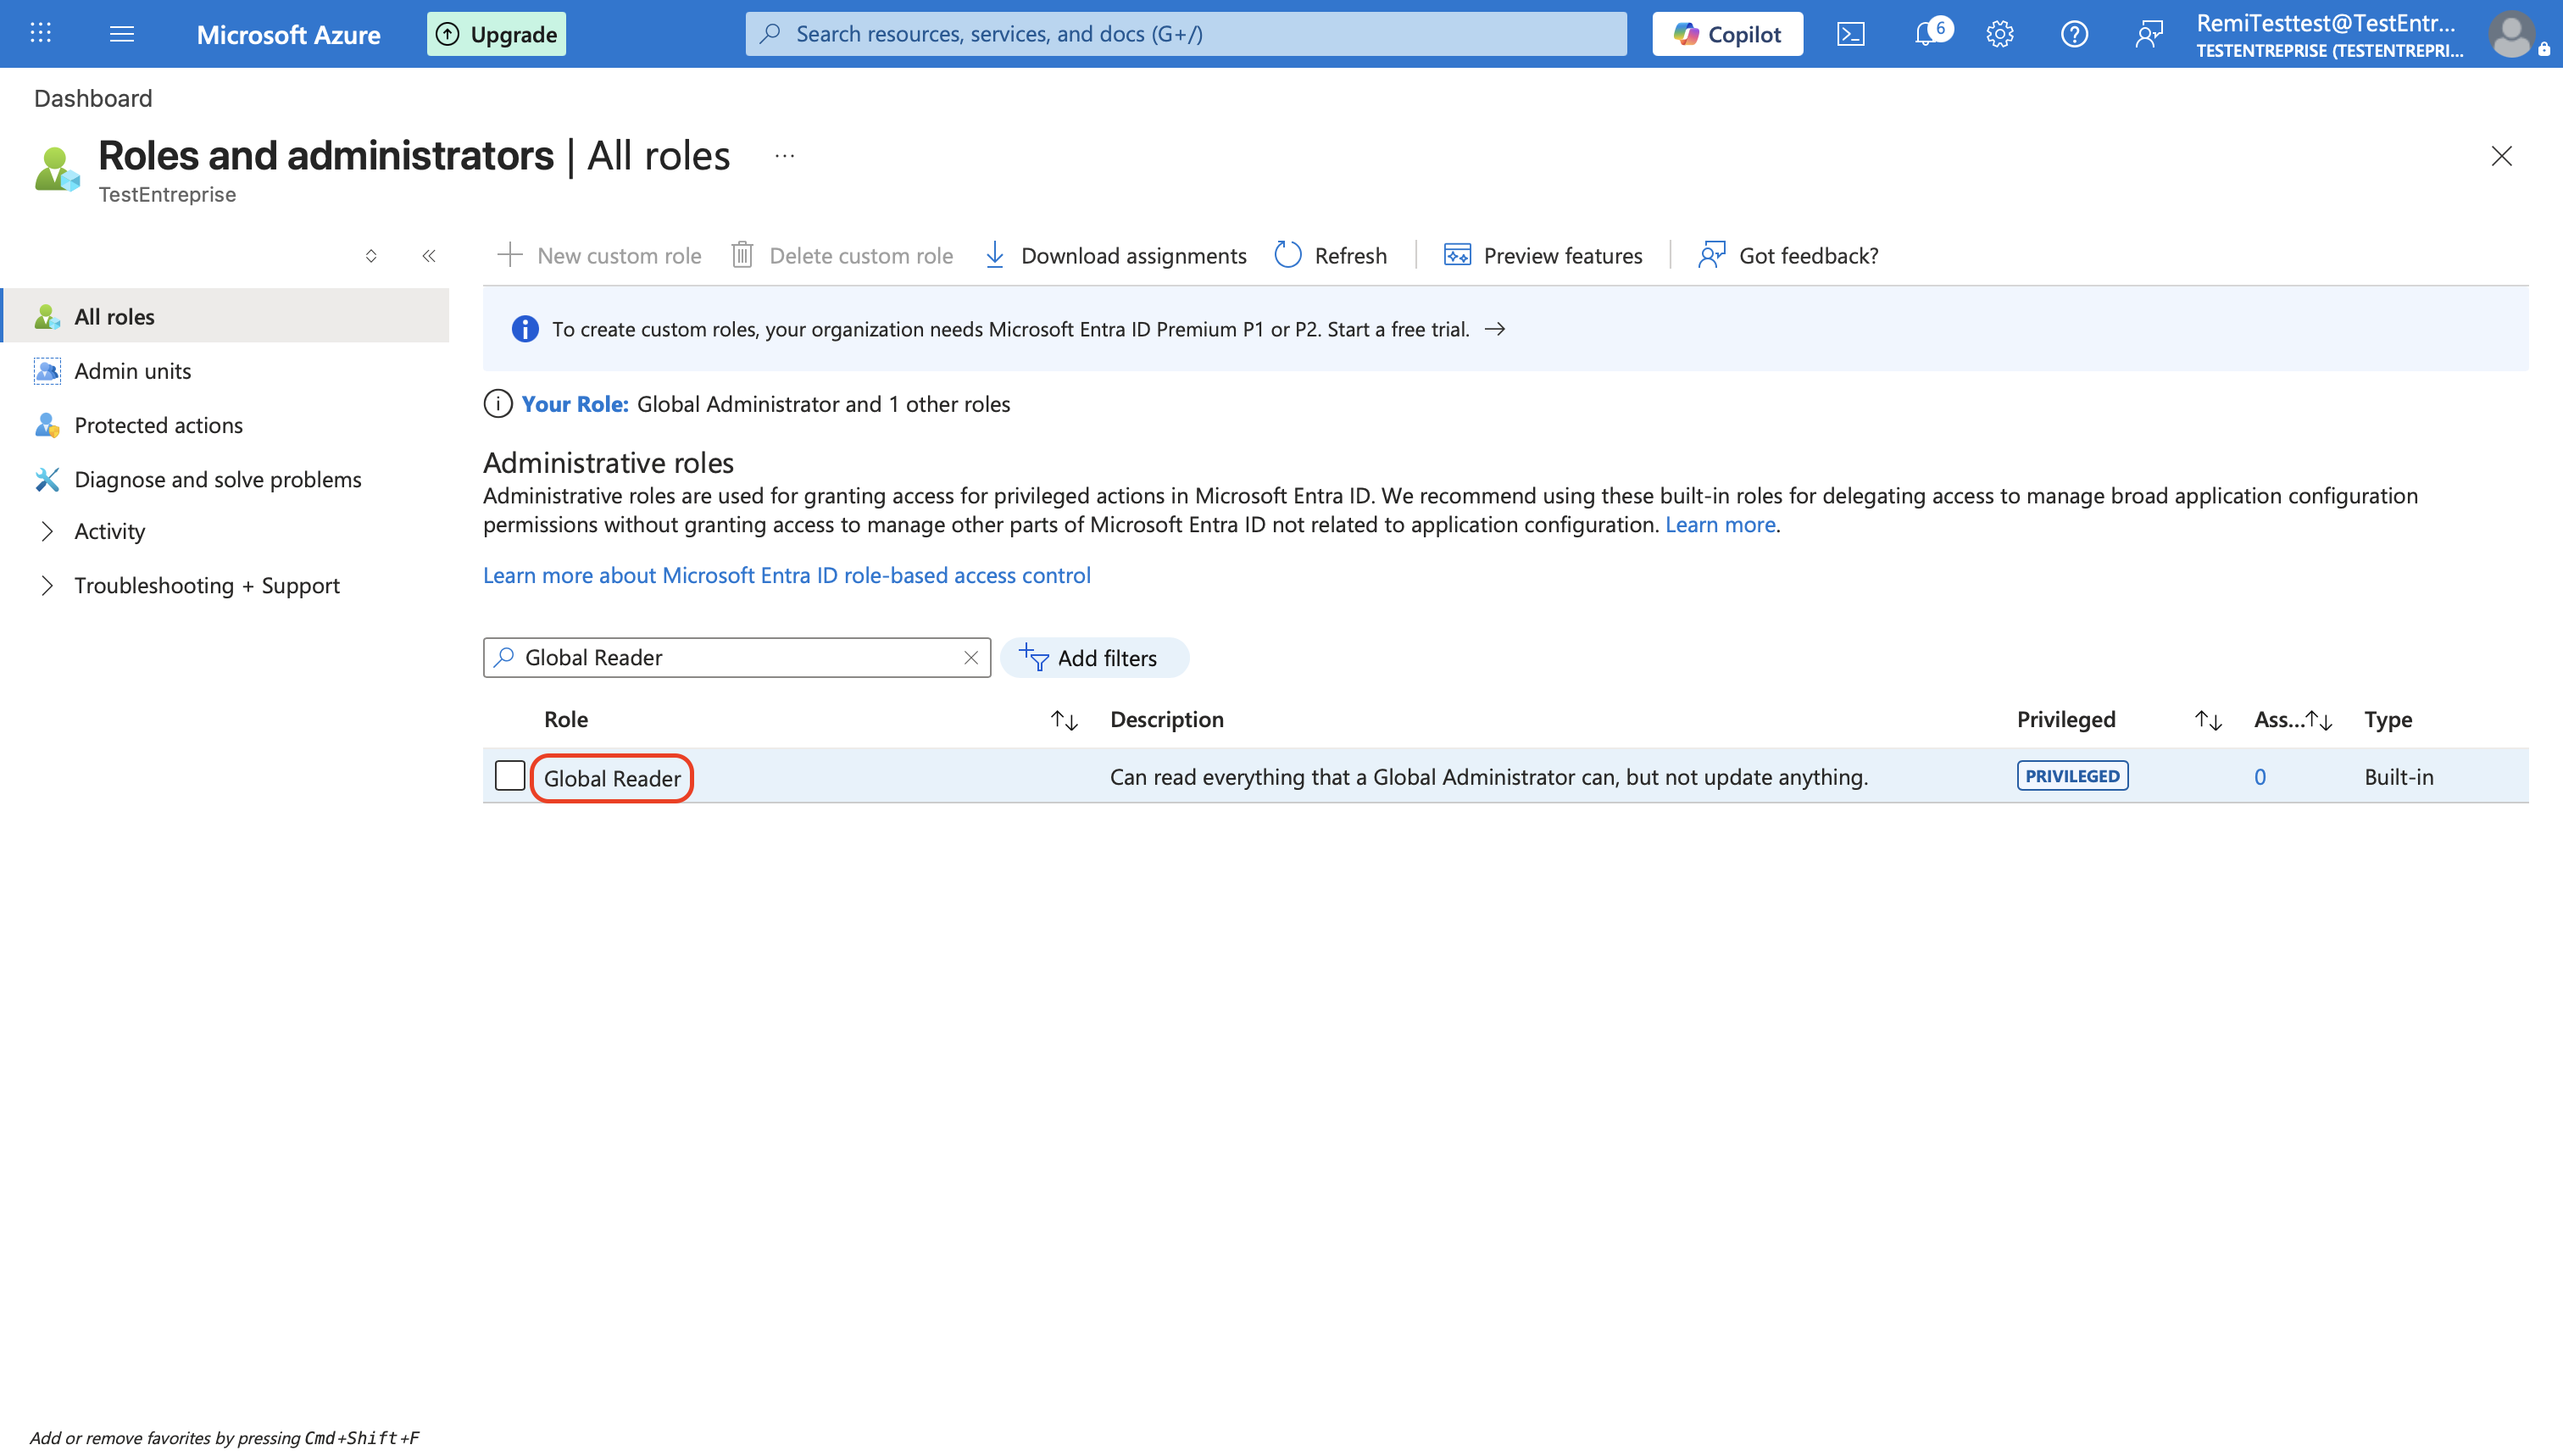
2. Search for the `Global Reader` role and click on it.
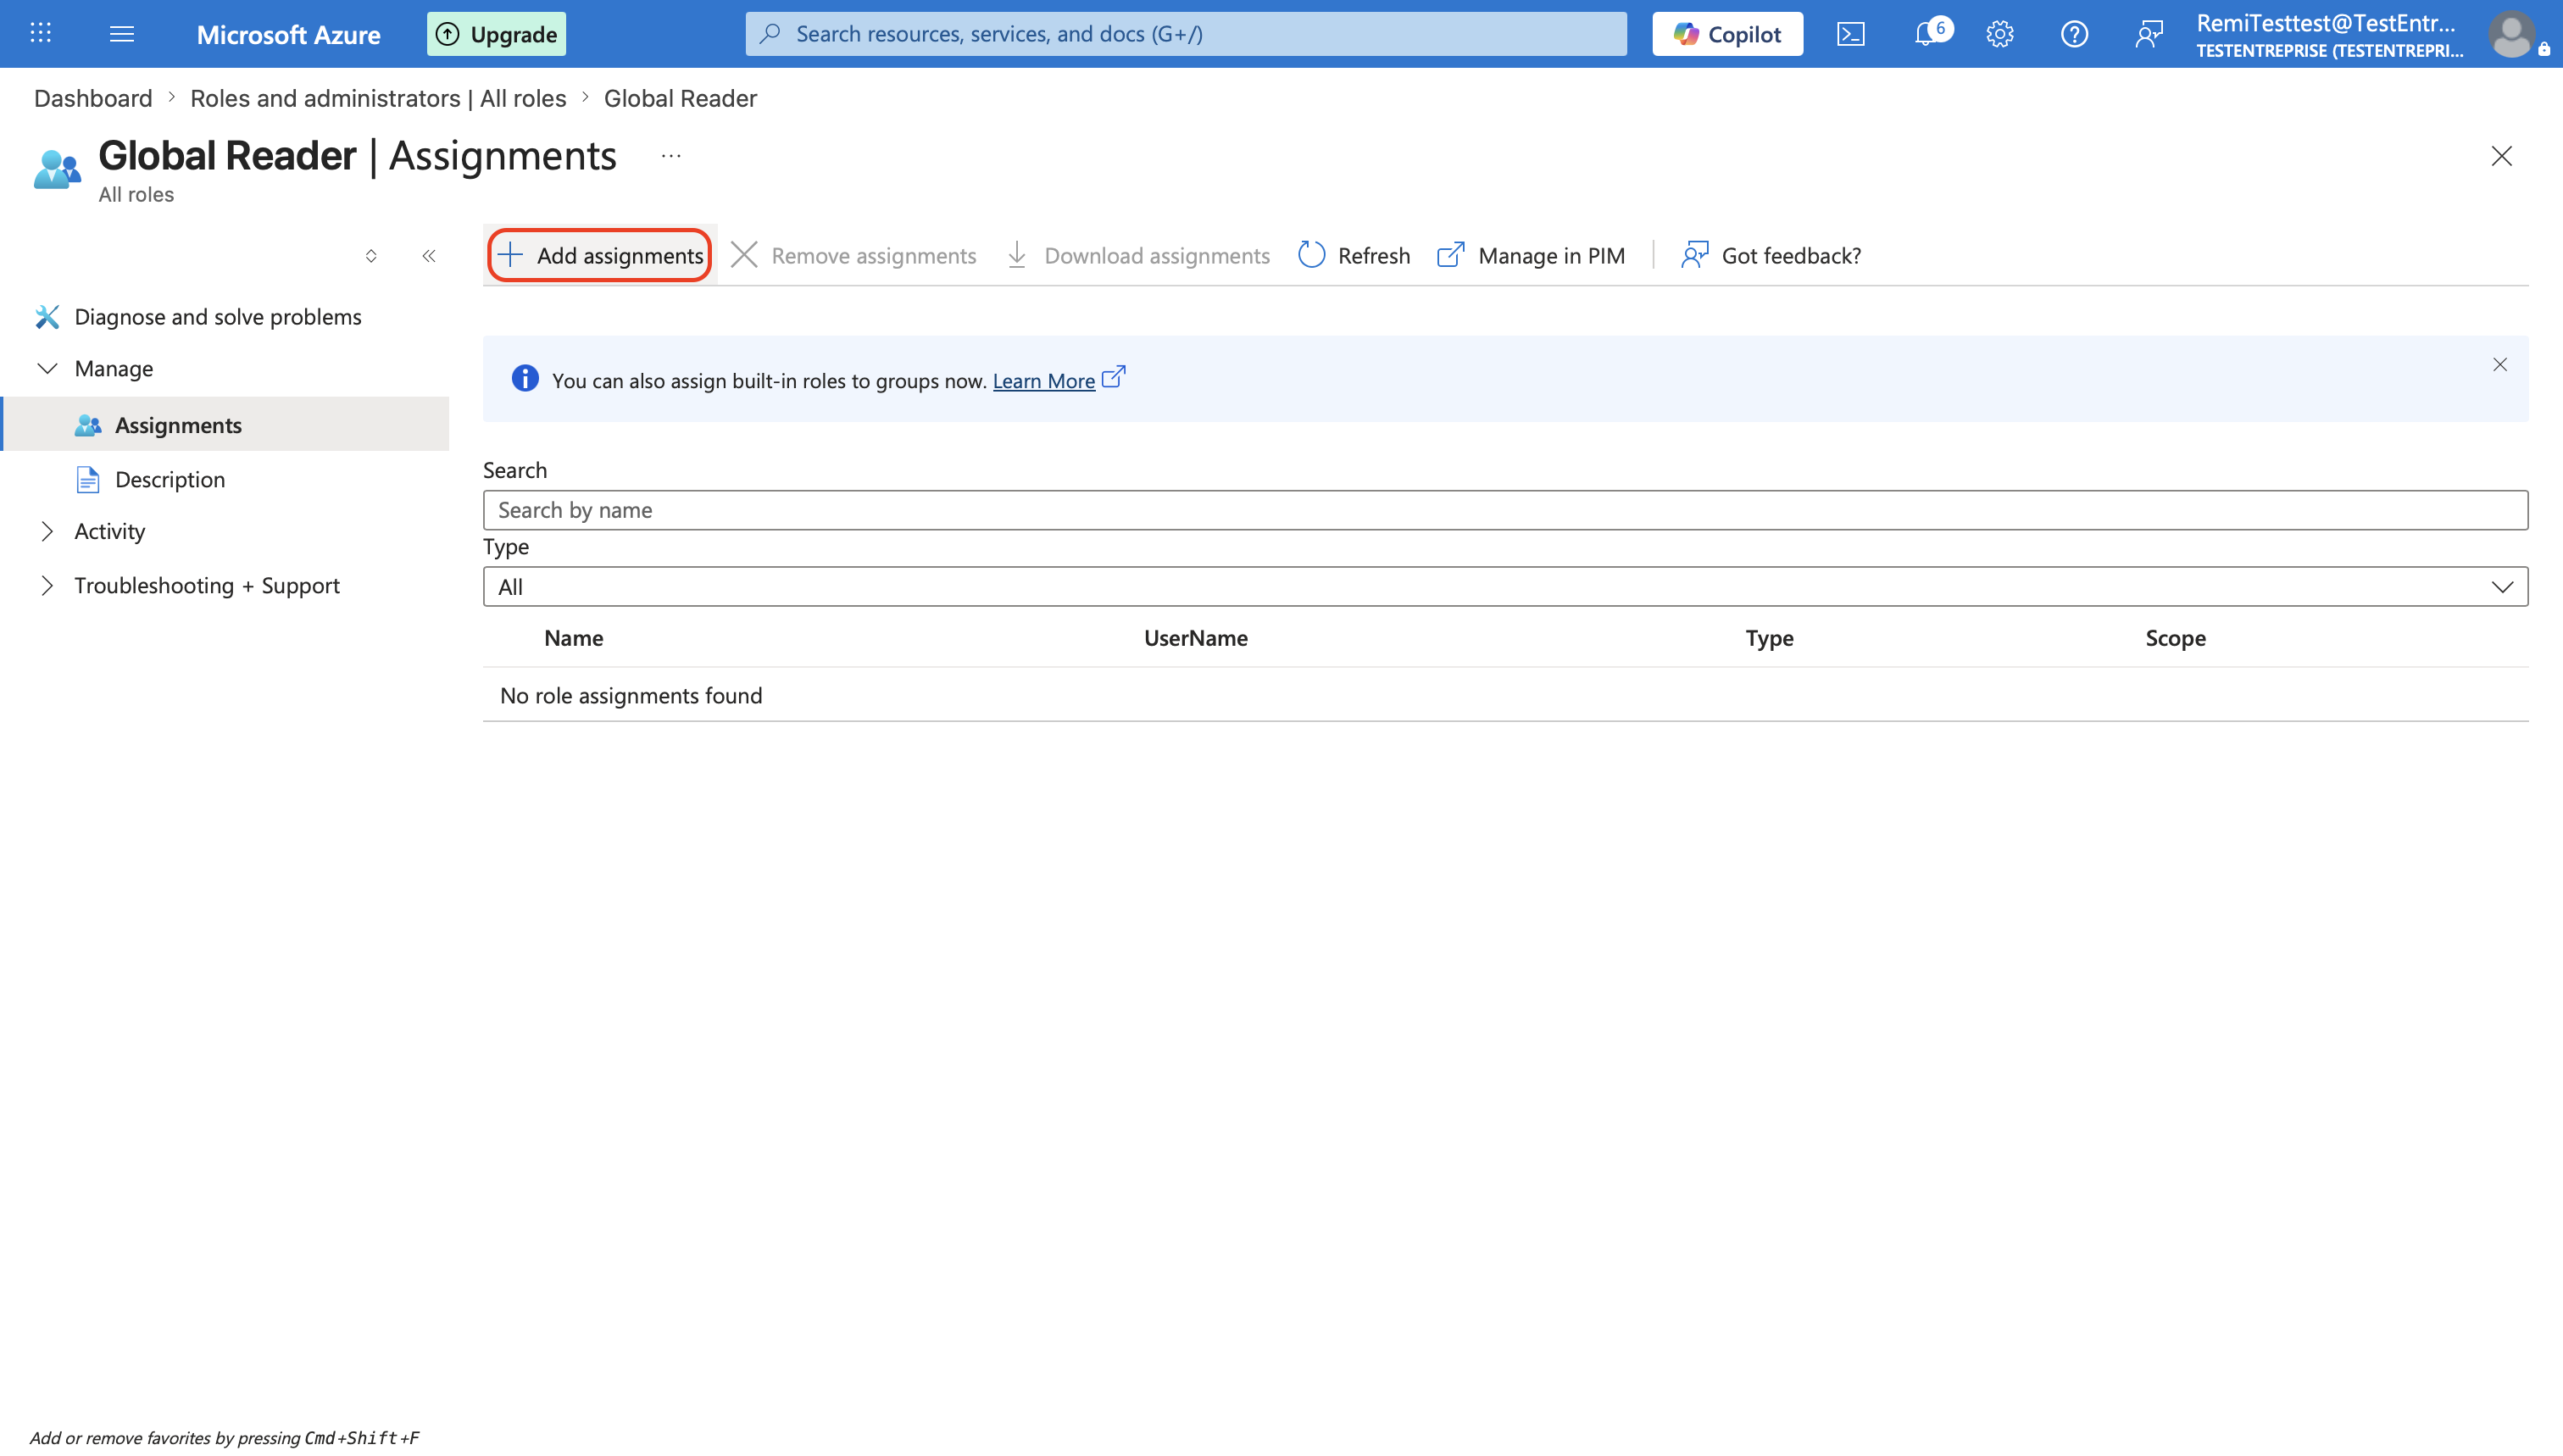
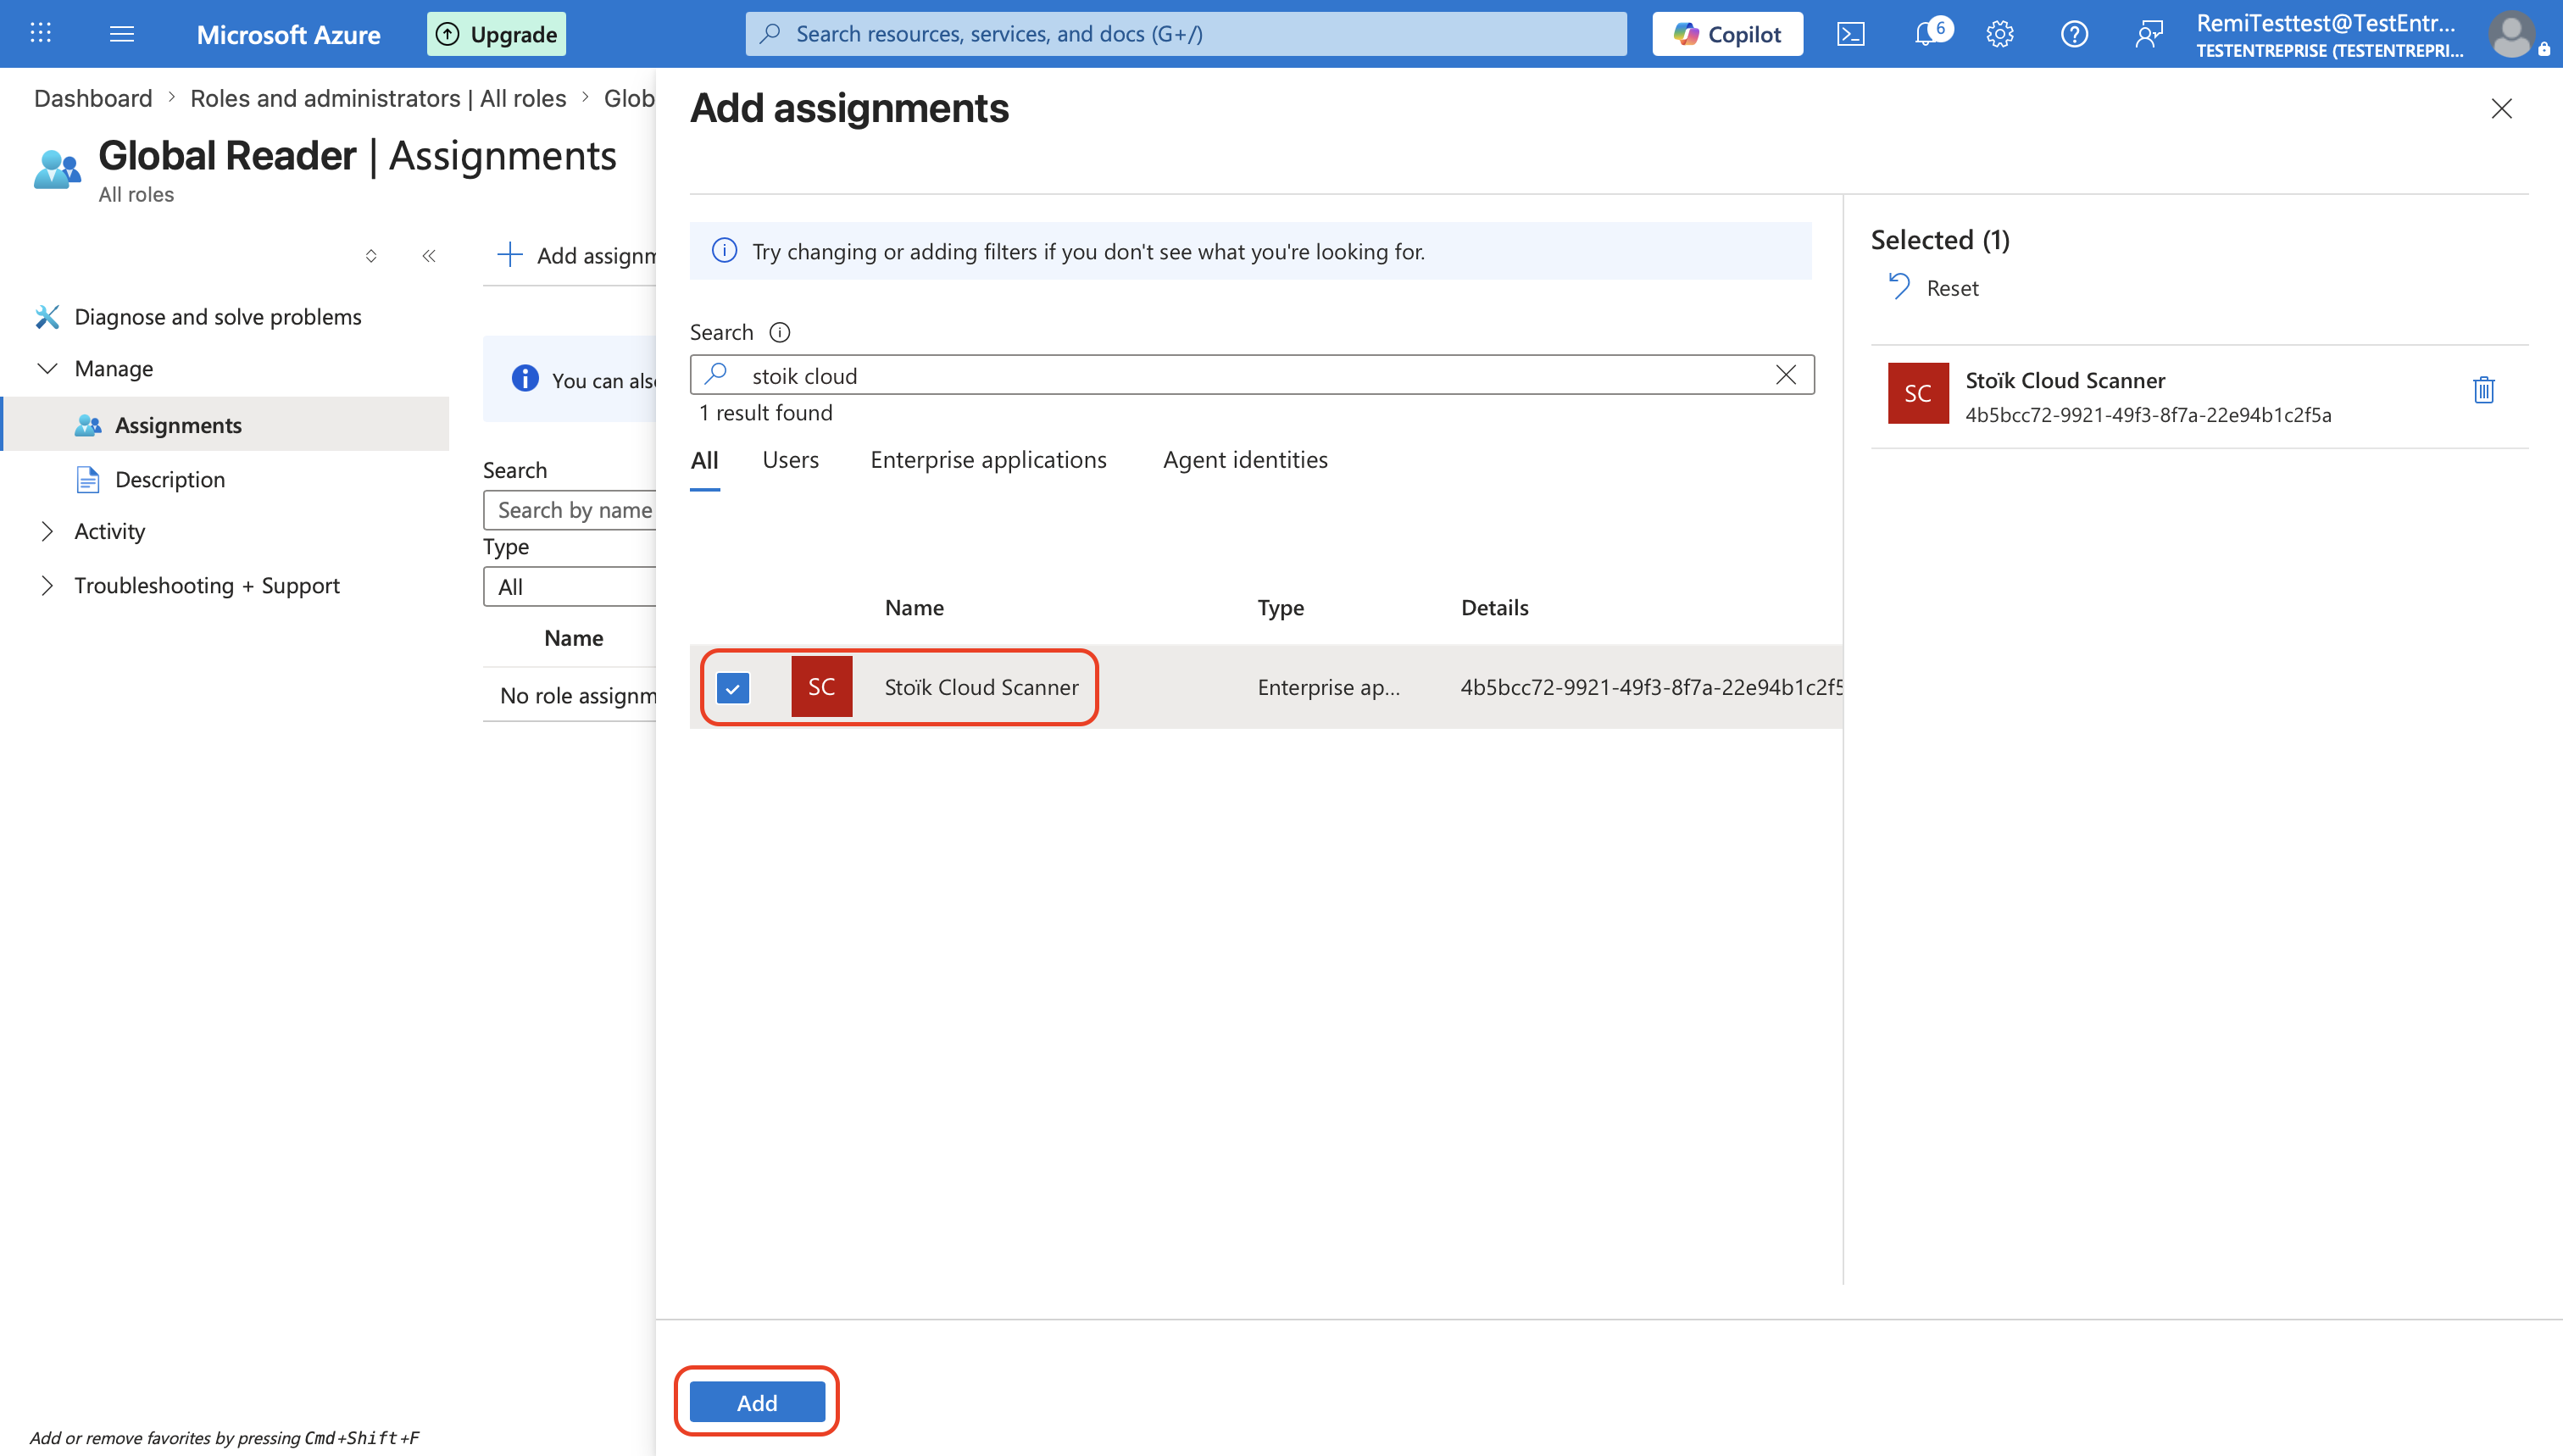
3. Click `Add assignments`, search for `Stoïk Cloud Scanner`, select it, then click `Add`.
4. Repeat steps 2 and 3 for the `Security Reader` role.
{% hint style="warning" %}
Do not grant additional rights such as `Global Secure Access Administrator`, otherwise it will not work.
{% endhint %}
{% endstep %}
{% step %}
### Complete setup
Click `Finish` in the Stoïk Protect console.
{% hint style="info" %}
Refresh the Stoïk Protect page if necessary.
{% endhint %}
{% endstep %}
{% endstepper %}
## Troubleshooting
Policy.Read.All cannot be granted, or a permission is missing
If you get "Policy.Read.All cannot be granted", or if `Reports.Read.All` or `UserAuthenticationMethod.Read.All` is missing, these permissions cannot be added by hand. Grant admin consent to the Stoïk application again:
1. In [portal.azure.com](https://portal.azure.com), search for **Stoïk Cloud Scanner** (`Enterprise applications`).
2. Open `Security` > `Permissions`.
3. Click **Grant admin consent for \** and accept the popup.
Consent must cover the whole organization, not only the admin's own account. Without `Policy.Read.All`, Stoïk cannot read your Conditional Access policies, which affects the [MFA findings](/prevention-tools/cloud-scan/results.md#mfa-findings-entra-id).
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://docs.stoik.io/prevention-tools/cloud-scan/entra-id.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.