> For the complete documentation index, see [llms.txt](https://docs.stoik.io/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.stoik.io/mdr/deploy/antivirus.md).
# Antivirus and exclusions
Uninstall any existing antivirus or other EDR solution before installing your Stoïk MDR EDR (CrowdStrike or SentinelOne), to prevent conflicts that could compromise the proper functioning of the solution.
## When to uninstall
{% tabs %}
{% tab title="CrowdStrike" %}
The Stoïk teams have implemented a gradual [three-phase deployment](/mdr/deploy/crowdstrike.md#deployment-phases) to limit the risk of blockages and the impact on user workstations. Phase 1 lets you install the EDR while keeping your antivirus or EDR in place, so you must uninstall your previous antivirus or EDR solution before moving on to phase 2.
{% hint style="warning" %}
If you do not uninstall it before moving on to phase 2, a "blue screen" may appear when the workstation is restarted.
{% endhint %}
However, some antivirus or EDR solutions, whether single-use or multi-use, may cause blockages as early as phase 1 of the deployment: see [Single-use antivirus](#single-use-antivirus) and [Multi-purpose solutions](#multi-purpose-solutions).
{% endtab %}
{% tab title="SentinelOne" %}
SentinelOne does not use a phased deployment: full protection is active as soon as it is installed. Uninstall your previous antivirus or EDR solution before installing SentinelOne, to avoid any conflict.
{% endtab %}
{% endtabs %}
## Single-use antivirus
These programs have only one function: antivirus protection.
{% tabs %}
{% tab title="CrowdStrike" %}
* **Bitdefender**: must be uninstalled during phase 1 of deployment. If you do not uninstall it, a blue screen may occur when you restart your computer.
* **Trend Micro**: must be uninstalled starting from deployment phase 2, otherwise error messages may appear.
* **macOS**: No known conflicts, no action required.
{% endtab %}
{% tab title="SentinelOne" %}
* **Bitdefender** and **Trend Micro**: must be uninstalled before installation, since SentinelOne has no phased deployment.
* **macOS**: No known conflicts, no action required.
{% endtab %}
{% endtabs %}
## Multi-purpose solutions
These software programs offer several security functions in a single tool: antivirus, firewall, USB device control, integrated EDR, etc. Common examples include **WithSecure**, **ESET**, and **Kaspersky**.
{% tabs %}
{% tab title="CrowdStrike" %}
Disable the antivirus functionality only. There is no need to uninstall the entire software.
There is no need to uninstall **Windows Defender**: it is fully compatible with your EDR. It remains active in phase 1, and the antivirus engine is disabled automatically at phase 2.
{% endtab %}
{% tab title="SentinelOne" %}
These solutions must be fully uninstalled before installing SentinelOne, since there is no phased deployment to tolerate a temporary conflict.
The only exception is **Windows Defender**: there is no need to uninstall it, it is fully compatible with SentinelOne, and the antivirus engine is disabled automatically as soon as SentinelOne is installed.
{% endtab %}
{% endtabs %}
{% hint style="warning" %}
Beware of side effects on Windows. If you completely disable the multi-purpose solution, and it previously managed your firewall, then:
* The [Windows Firewall](https://learn.microsoft.com/en-us/windows/security/operating-system-security/network-security/windows-firewall/) will automatically take over.
* However, it will apply its own default, very restrictive rules.
* This can completely block your network connections.
The solution is to reconfigure your local Windows firewall with the necessary rules and exclusions to restore the expected connections.
{% endhint %}
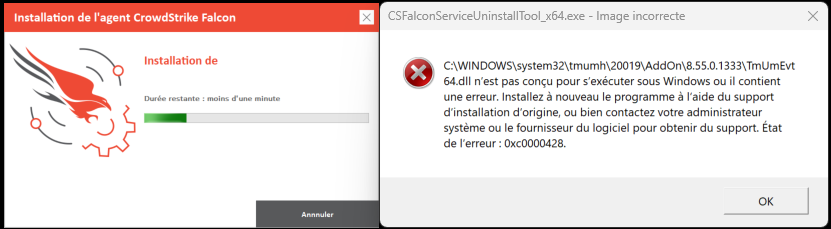
Example of an error message:
## Exclusion rules
Managing application flows through exclusion rules is an approach specific to traditional antivirus solutions, but it does **not** apply to an EDR such as **CrowdStrike** or **SentinelOne**.
### Difference in operation between antivirus and EDR
* **Antivirus:** proactively scans all dormant files on the system (whether executed or not). This generates a large volume of scans and requires numerous exclusions to avoid false positives on inactive files.
* **EDR (CrowdStrike, SentinelOne):** focuses only on files that are actually executed and on dynamic system behaviors (processes, connections, user actions, etc.). No continuous full-disk scanning is performed. Inactive files are not analyzed except during manual scans.
Since an EDR analyzes **suspicious behaviors rather than signatures**, excluding a folder from analysis is unnecessary.
{% hint style="warning" %}
Excluding a folder would have a negative effect: if suspicious behavior were to occur in that folder, the EDR would not be able to detect it. That said, this remains technically possible if the need is validated by our SOC team.
{% endhint %}
### Intelligent prevention and reactive exclusion management
Your EDR integrates a set of preventive mechanisms to limit false positives without manual intervention:
* Preconfigured exclusion lists are automatically applied during deployment.
* In the event of a suspicious detection involving a business application, the program is temporarily blocked, then analyzed by our SOC before any definitive action is taken.
{% hint style="warning" %}
To avoid potential unwanted business disruptions, full isolation is performed **only manually**, either after analysis by our SOC team or by you.
{% endhint %}
### Exclusions should not be defined upfront
Trying to anticipate exclusions before any detection occurs represents a major risk:
* It amounts to preemptively excluding potentially malicious behaviors simply because they are associated with a known business application.
* **Result:** you risk neutralizing the EDR's detection capabilities, allowing certain attacks to go undetected.
Exclusions in an EDR are far fewer. At **Stoïk**, they are handled **only in response to a real detection**, when a blocking event has actually occurred, based on SOC analysis. It is neither necessary nor advisable to add "preventive" exclusion rules as you would with a traditional antivirus.
**Concrete example:** One of our clients (a national retail player) had more than 3,000 workstations and several thousand exclusions in their previous antivirus solution. After switching to an EDR, no exclusions were required.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://docs.stoik.io/mdr/deploy/antivirus.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.