

Device Control
The Device Control module allows you to control the use of USB devices (USB keys, hard drives, etc.). Device Control lets you create a USB device Policy: you define general rules that allow or block USB devices based on their class.
What is possible:
Configuration by device type
Implemented using CrowdStrike Policies, either by you or by the Stoïk SOC
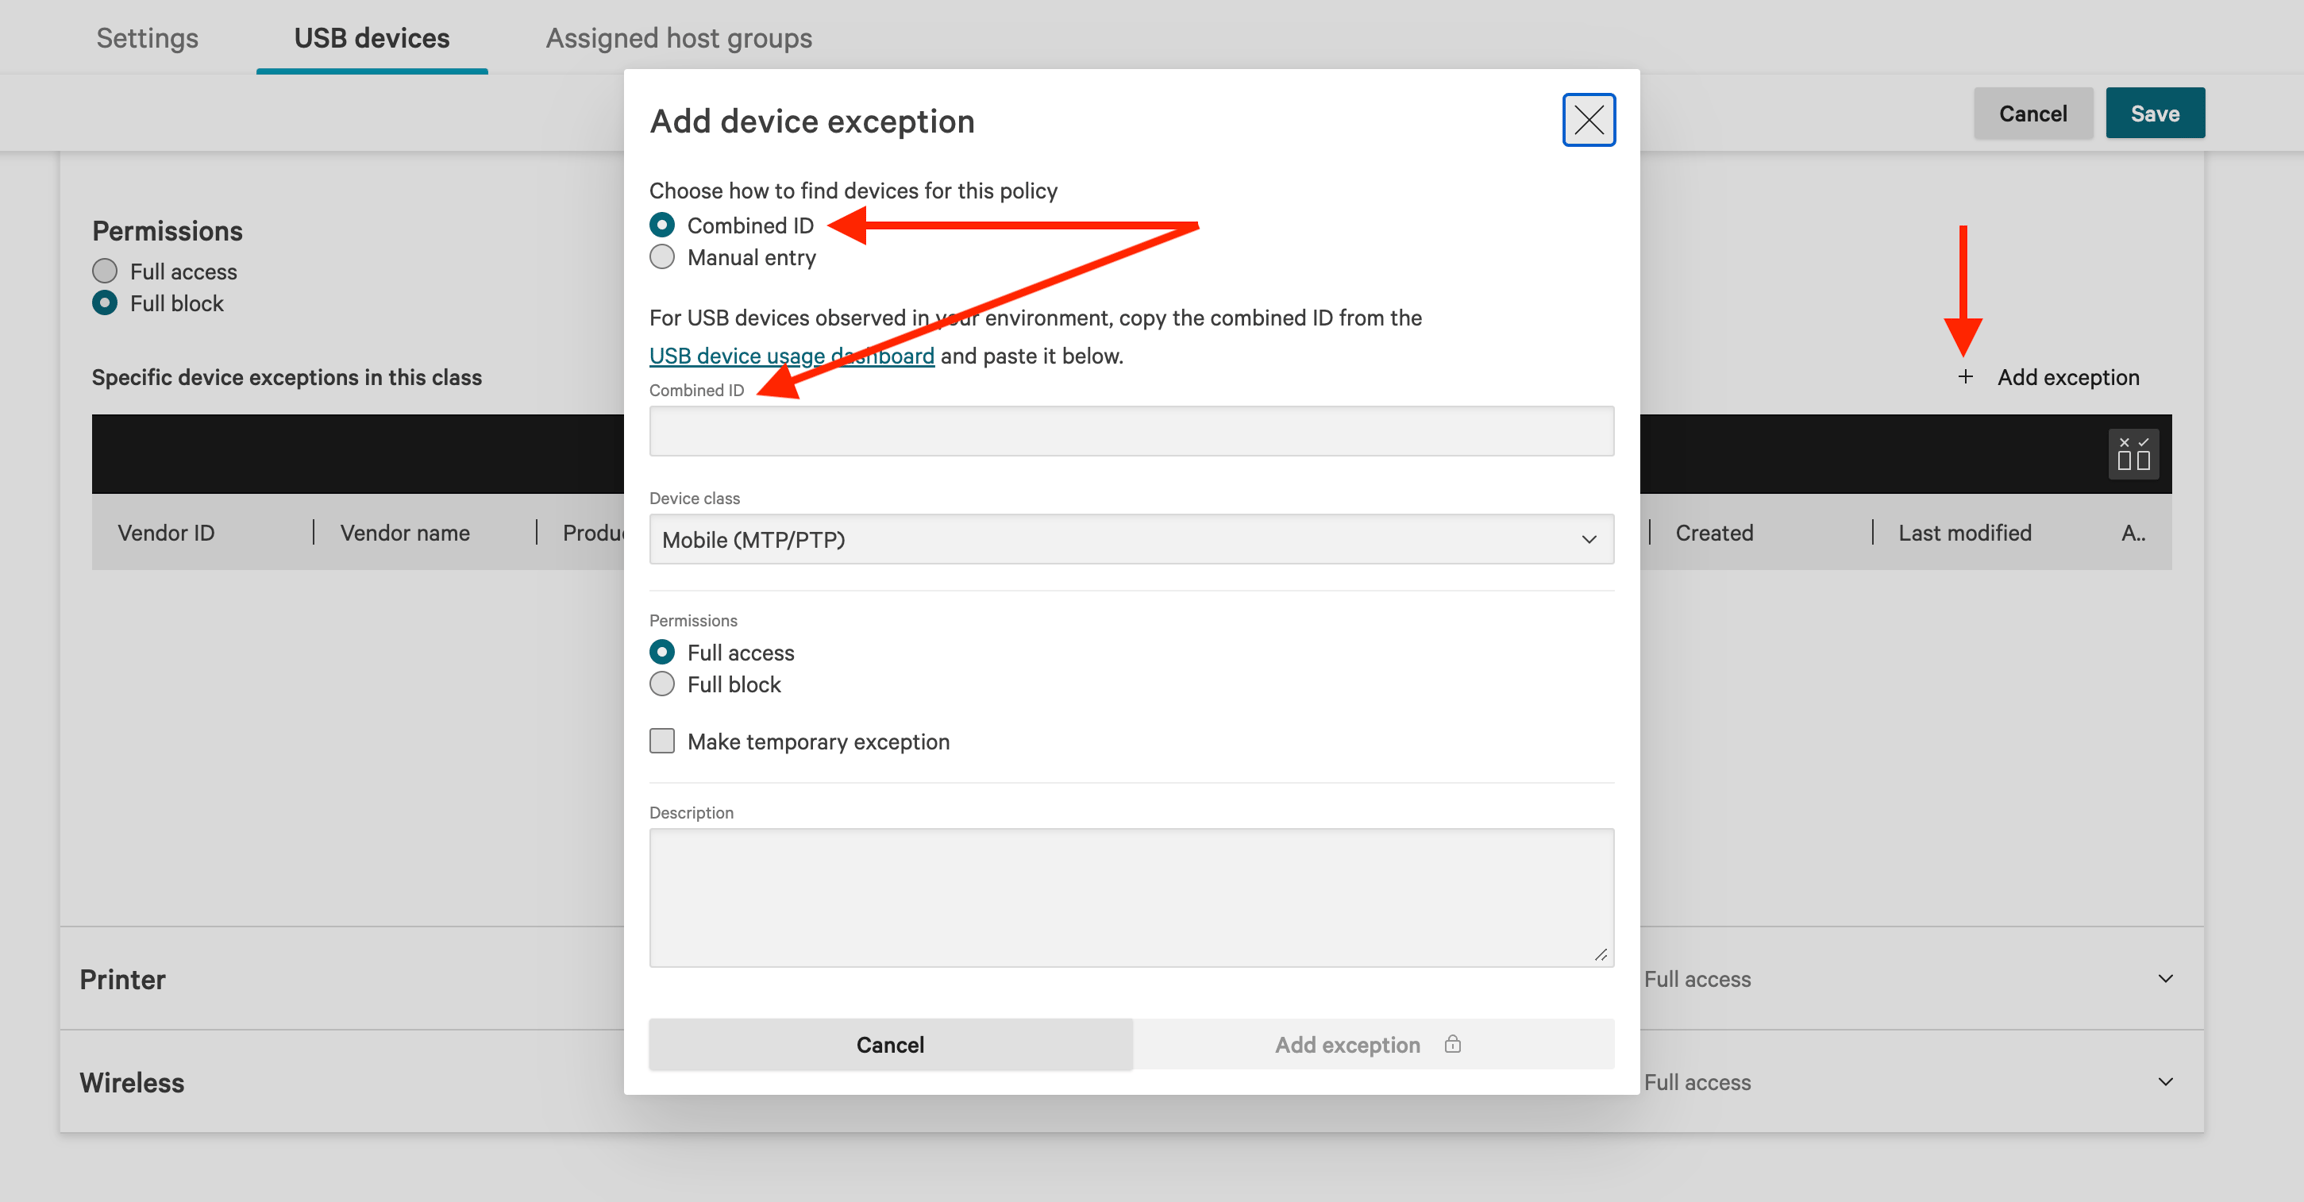
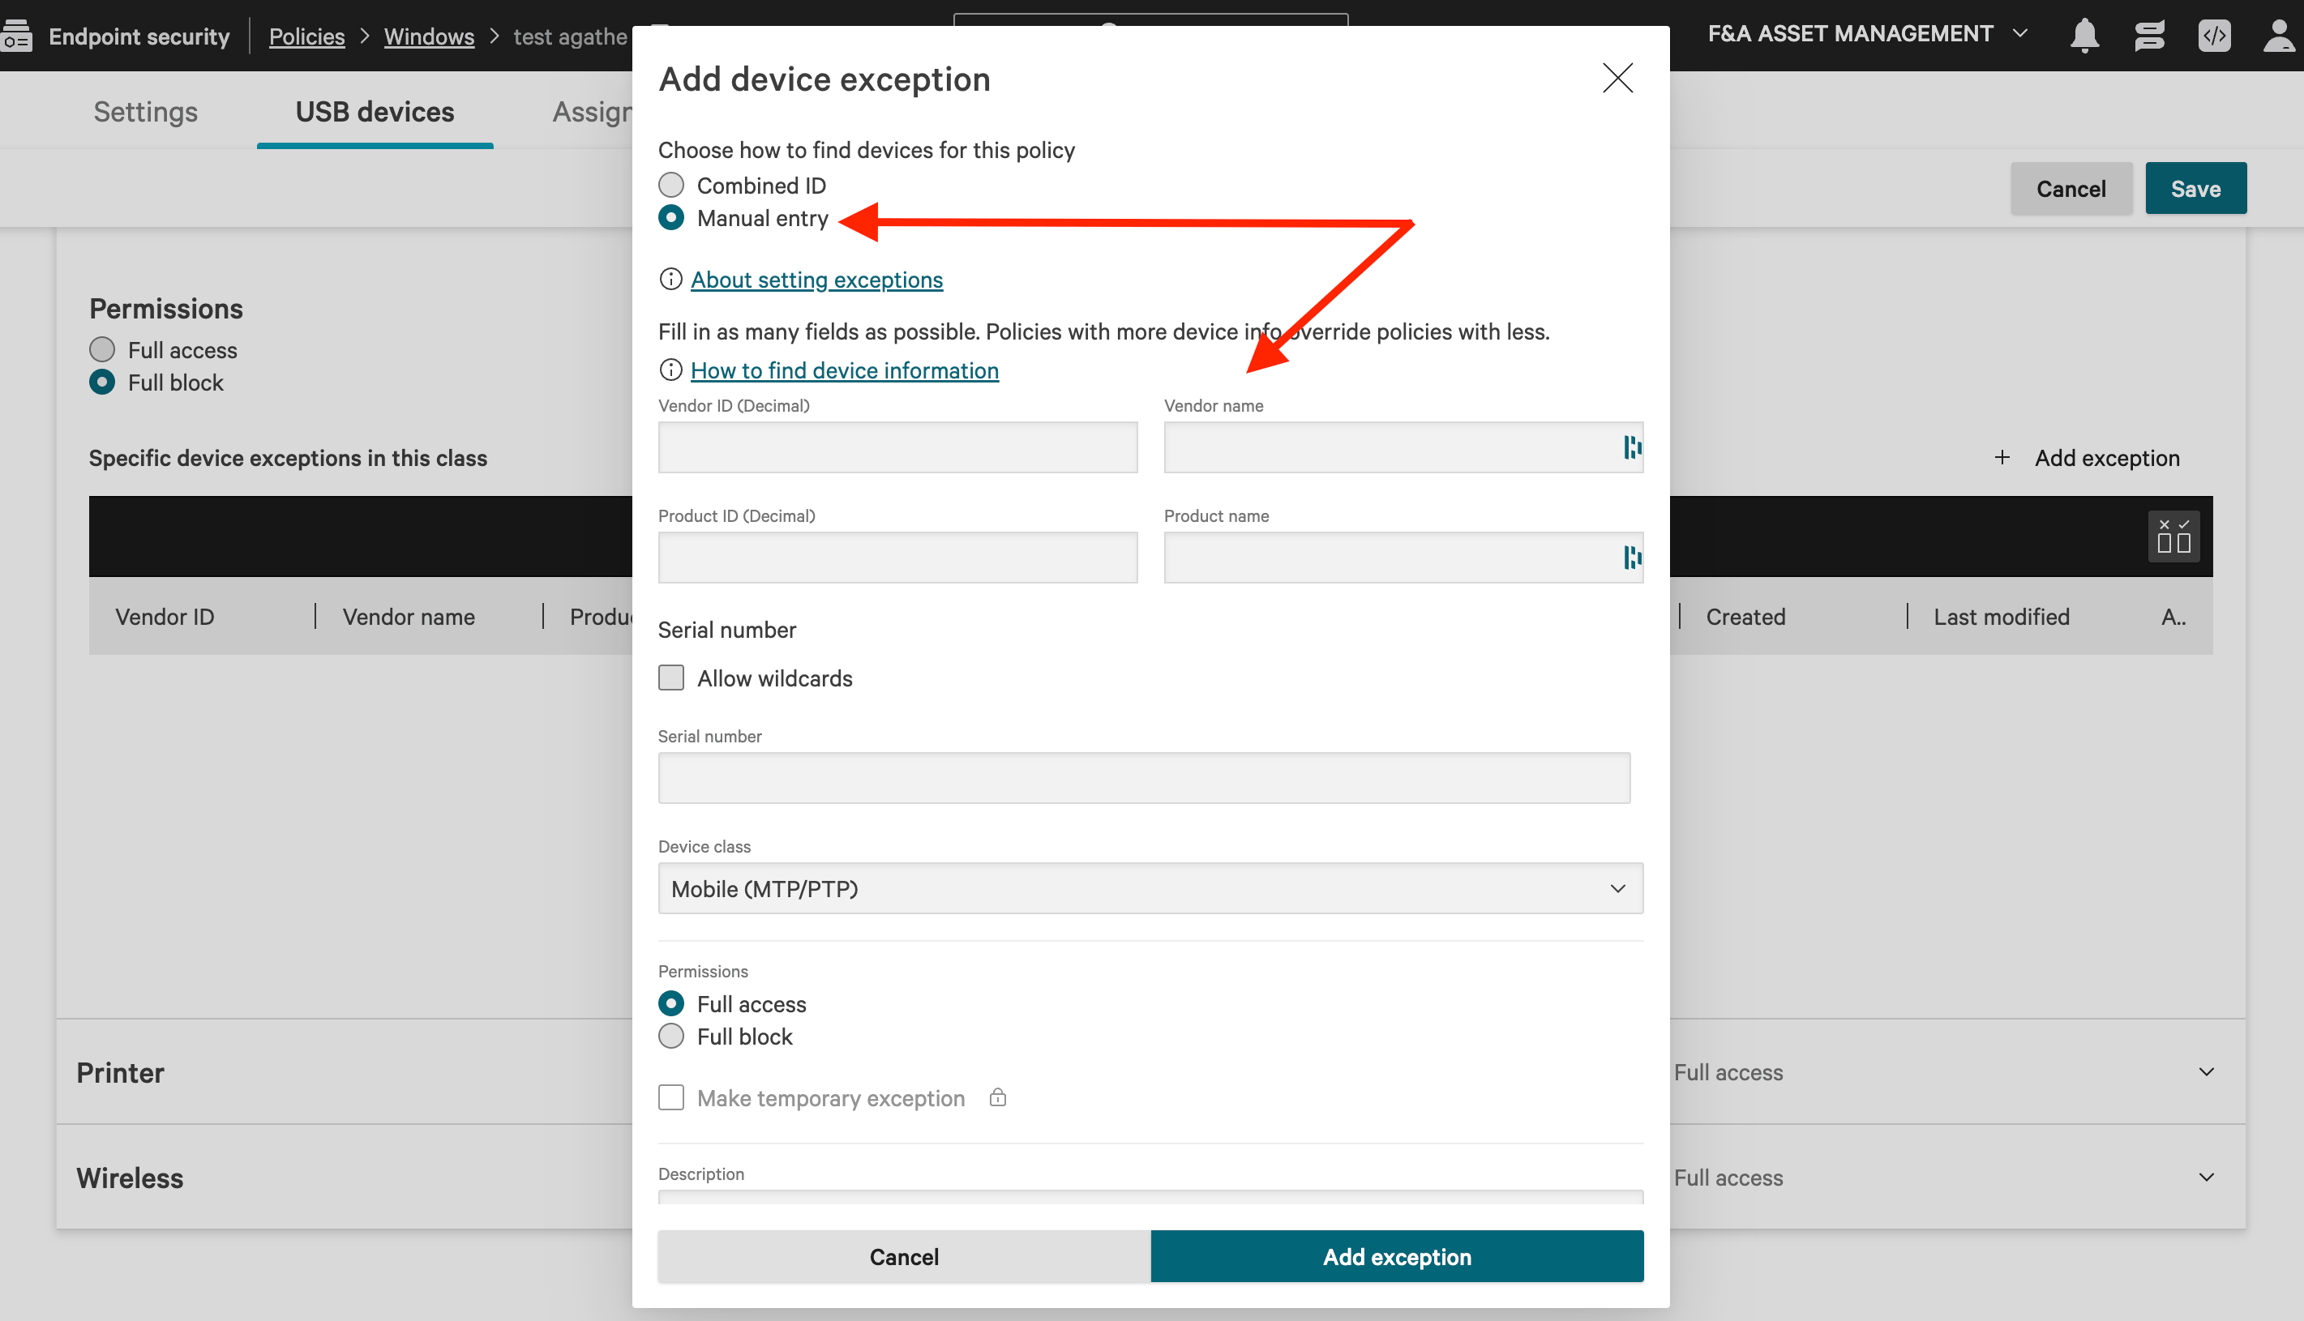
Configuration of exclusions (workstation, device)
Can be managed with the
Device Control Manageruser right
What is not possible:
Configuration by endpoint (this would require assigning each endpoint to specific groups)
For example, you can create a policy to block USB storage devices while allowing access to other USB device classes.
Deployment
Define your control objectives
Determine what you want to enforce:
Block all USB devices
Set devices to read-only
Allow only specific models
Monitor / audit usage without blocking (observation mode)
Inventory of authorized or blocked devices
For each USB device you want to allow or block:
Plug it into a workstation.
Retrieve its hardware identifiers.
Via the graphical interface:
Device Manager > USB device > right-click > Properties > Details > Hardware IDs
Via PowerShell:
Get-PnpDevice -PresentOnly | Where-Object { $_.Class -eq "USB" }Send the following information to protect@stoik.io:
Vendor ID (VID)
Product ID (PID)
Serial number (if applicable)
Stoïk team configuration
A Stoïk cybersecurity engineer configures the rules and informs you once the setup is complete.
Create and configure the policy
Click
Create policy, enter a name and optional description, then clickCreate policyto confirm.In the
Settingstab:Select the mode (
Monitor,Monitor and enforce, orOfffor macOS only).Enable the desired USB settings.
Select the notification to inform end users when a USB device is fully blocked.
Select the notification to inform end users when a USB device is restricted.
In the
USB Devicetab, expand each device class to include, choose the authorization level, and add exceptions per class if needed by clickingAdd exception.
Activate the policy
Click
Savein the top-right corner, thenSaveagain to confirm.In the
Assigned host groupstab, clickAssign host groups to policy.Click
Enable policy.
To speed up configuration of similar policies, click Duplicate policy to create an exact copy.
Policy deployment
Device policies are applied as soon as a USB device is connected to a host. If USB devices are already connected at the time the policy is assigned, they will only be affected upon their next reconnection or the next host reboot.
Device policies are applied as soon as a USB or Bluetooth device is connected to a host. If devices are already connected at the time the policy is assigned, the policy takes effect immediately. If the policy blocks the device, it will be disconnected.
Last updated
Was this helpful?