> For the complete documentation index, see [llms.txt](https://docs.stoik.io/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.stoik.io/prevention-tools/cloud-scan/aws.md).
# Setup: AWS
Give the Cloud scan read-only access to an AWS account by creating a policy and a role, then pasting the role ARN in Stoïk Protect.
## Prerequisites
* An administrator account on the AWS account to scan.
* If you use AWS Organizations, your Service Control Policies (SCPs) must not block the read-only permissions below. SCPs are the most common cause of setup failures, see [Troubleshooting](#troubleshooting).
* A technical advisor is required for ongoing supervision and vulnerability remediation.
* One person does the whole setup, from start to finish: a Stoïk Protect user allowed to edit prevention tools, who is also an administrator of the AWS account.
## Setup
{% stepper %}
{% step %}
### Select Amazon Web Services
Go to `Cloud Scan` > `Settings`, click `New Provider`, and select `AWS`.
{% endstep %}
{% step %}
### Create a new policy
#### Configure the policy
1. Go to the [AWS policy creator](https://console.aws.amazon.com/iam/home?#/policies$new?step=edit) and log in with your administrator account.
2. Click the `JSON` tab and paste the following policy into the editor:
```json
{
"Version": "2012-10-17",
"Statement": [
{
"Effect": "Allow",
"Action": [
"ecr:BatchGetRepositoryScanningConfiguration",
"ecr:DescribeImageScanFindings",
"ecr:DescribeImages",
"dynamodb:ListTagsOfResource",
"ecr:ListTagsForResource",
"inspector2:BatchGet*",
"inspector2:Get*",
"inspector2:Describe*",
"inspector2:List*",
"sqs:ListQueueTags",
"sso:Describe*",
"sso:List*"
],
"Resource": "*"
},
{
"Effect": "Deny",
"Action": [
"datapipeline:EvaluateExpression",
"datapipeline:QueryObjects",
"rds:DownloadDBLogFilePortion"
],
"Resource": "*"
}
]
}
```
3. Click `Next`.
#### Save the policy
1. Name the policy `StoikAdditionalPermissions`.
2. Click `Create policy`.
{% endstep %}
{% step %}
### Create a new role
#### Configure the role trust
1. Go to the [AWS role creator](https://us-east-1.console.aws.amazon.com/iamv2/home#/roles/create?step=selectEntities).
2. Click `AWS account`, then `Another AWS account`, and enter the following account ID:
```
436578779424
```
3. Select `Require external ID` and copy the value displayed in the Stoïk Protect console.
4. Click `Next`.
#### Assign permissions and finalize
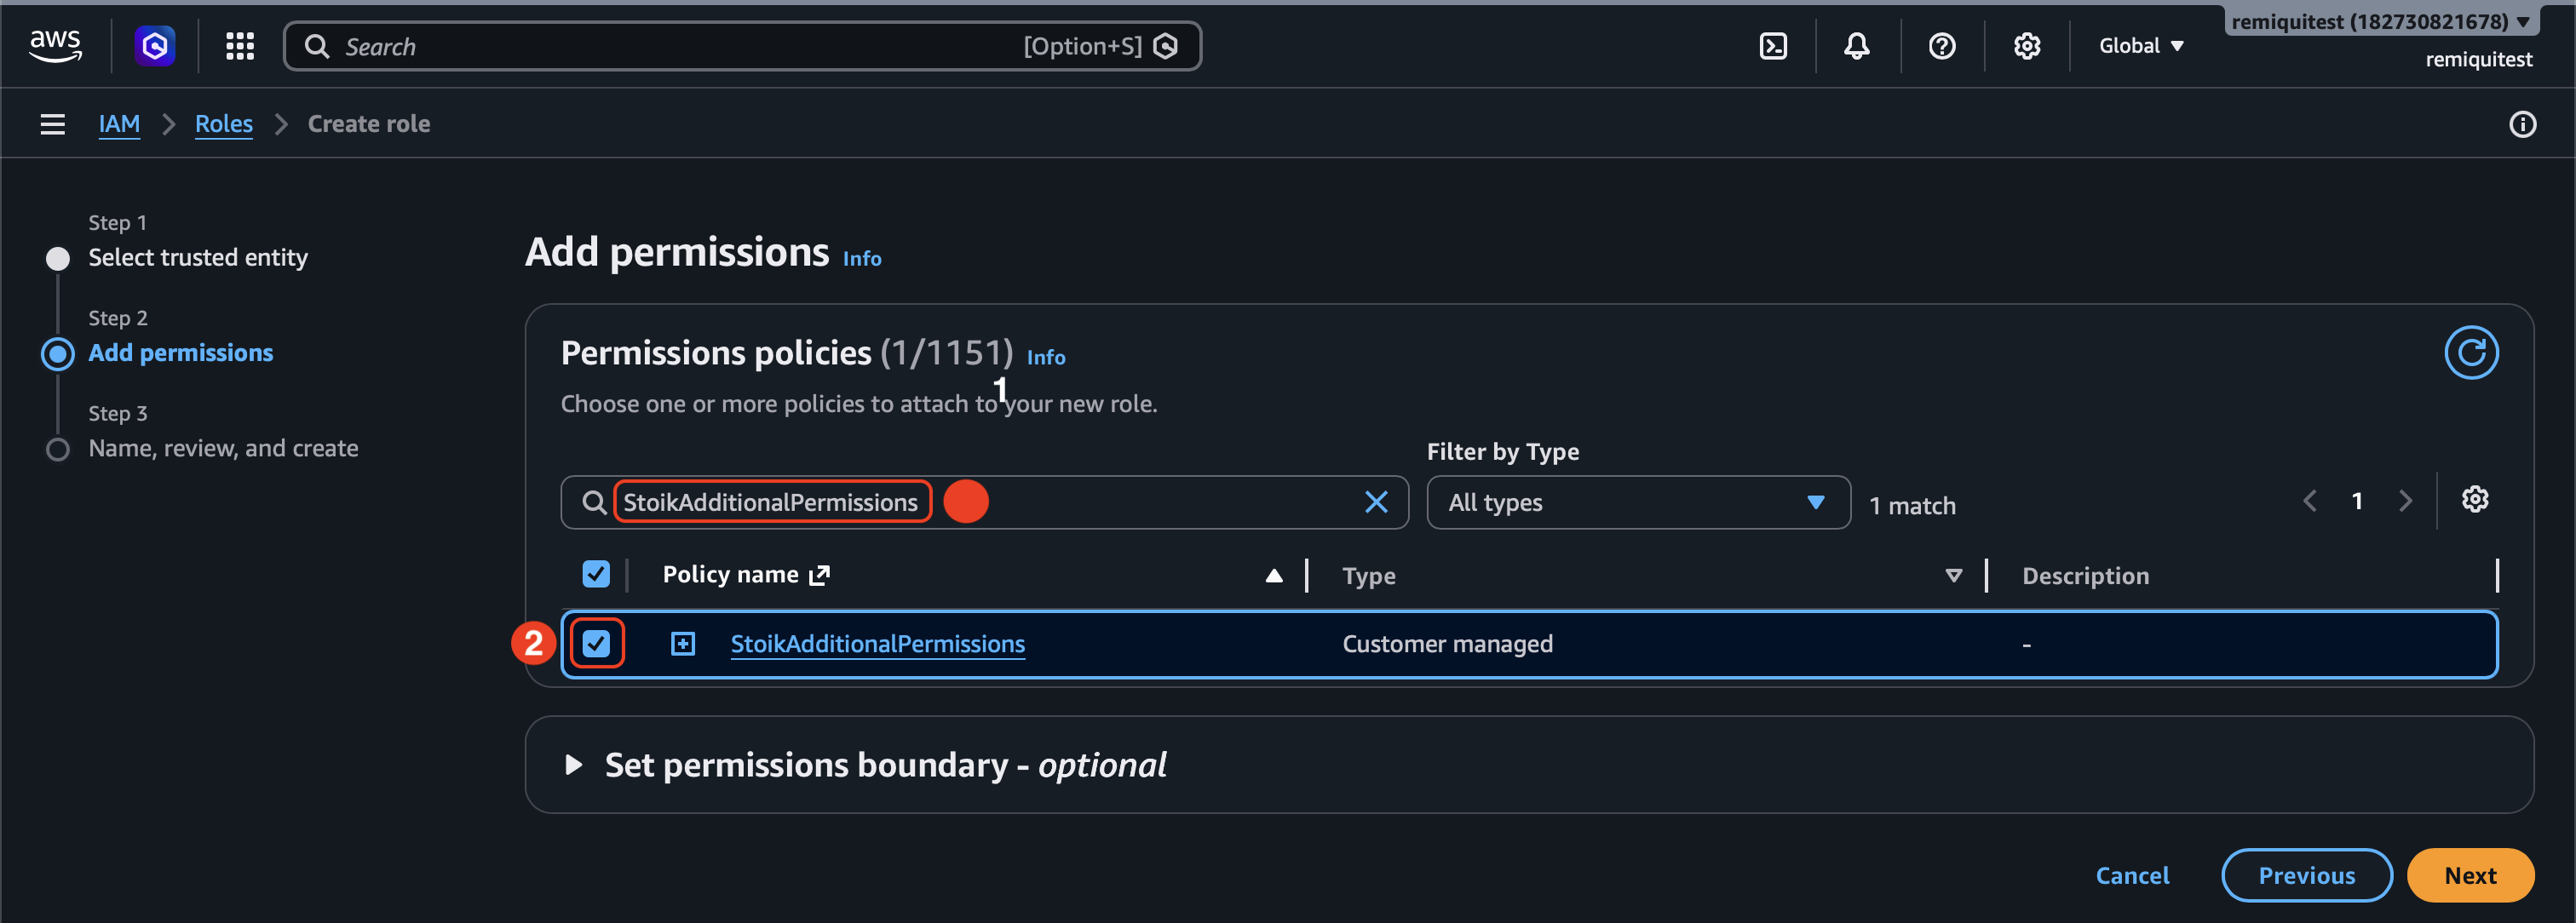
1. Select `StoikAdditionalPermissions` and `SecurityAudit` as permissions.
2. Click `Next`.
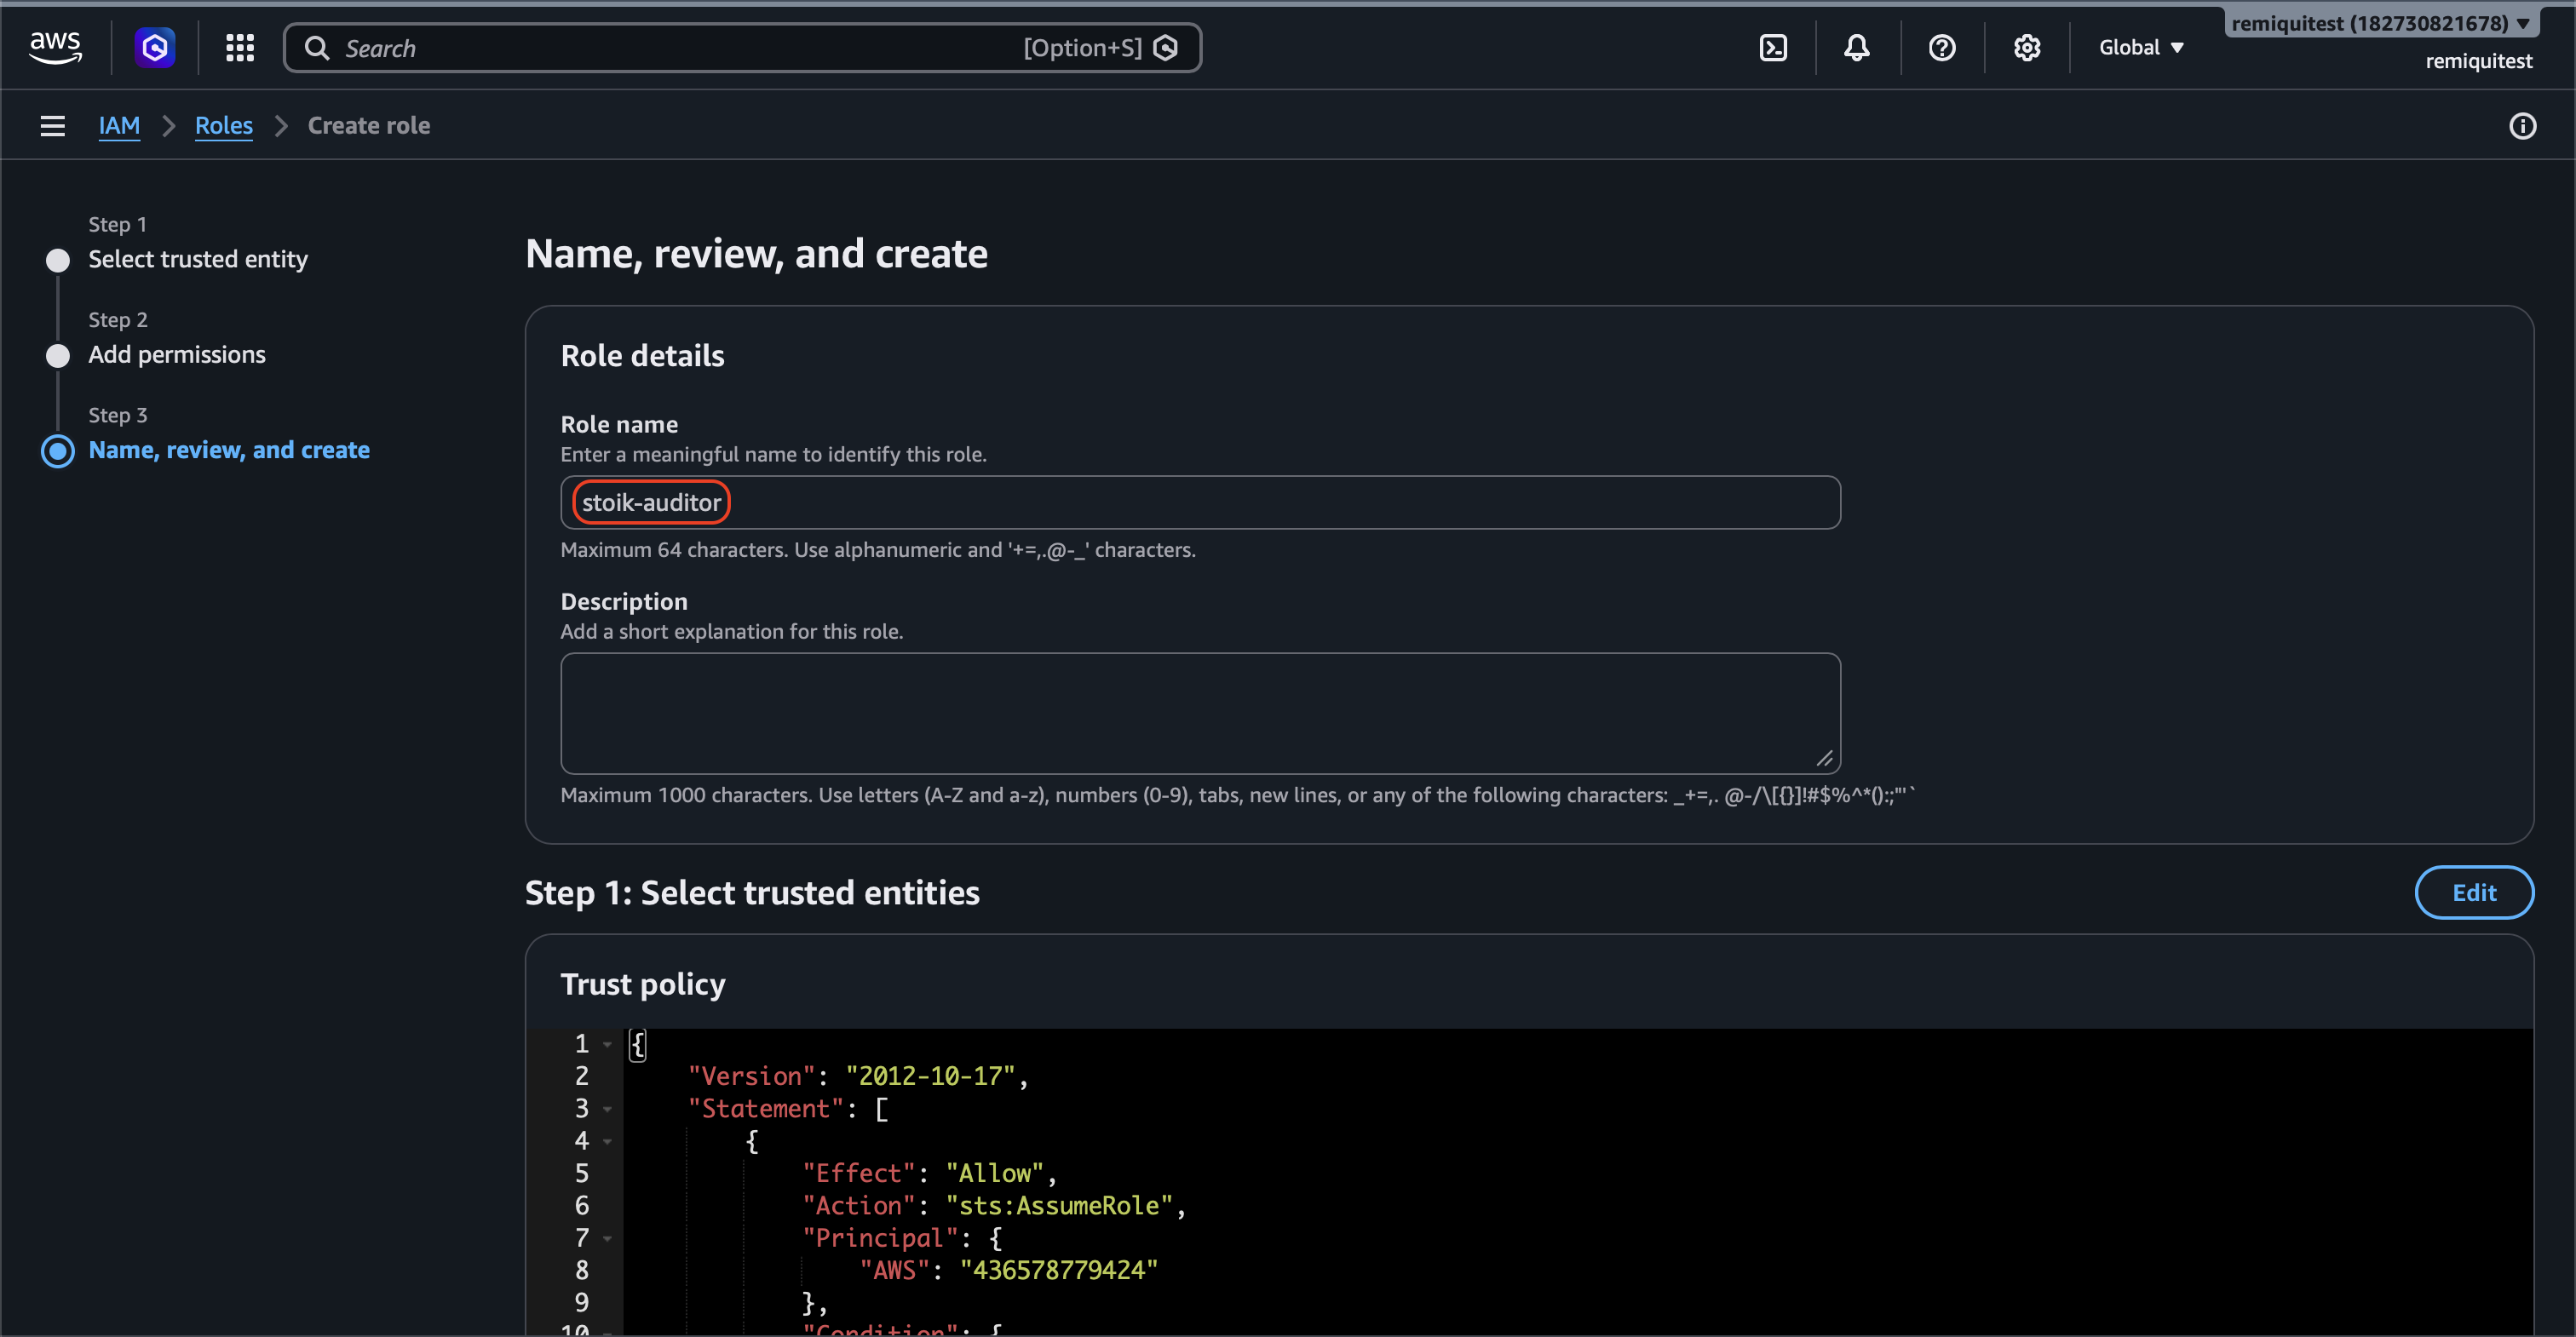
3. Enter `stoik-auditor` as the role name.
4. Click `Create role`.
{% endstep %}
{% step %}
### Add an ARN identifier
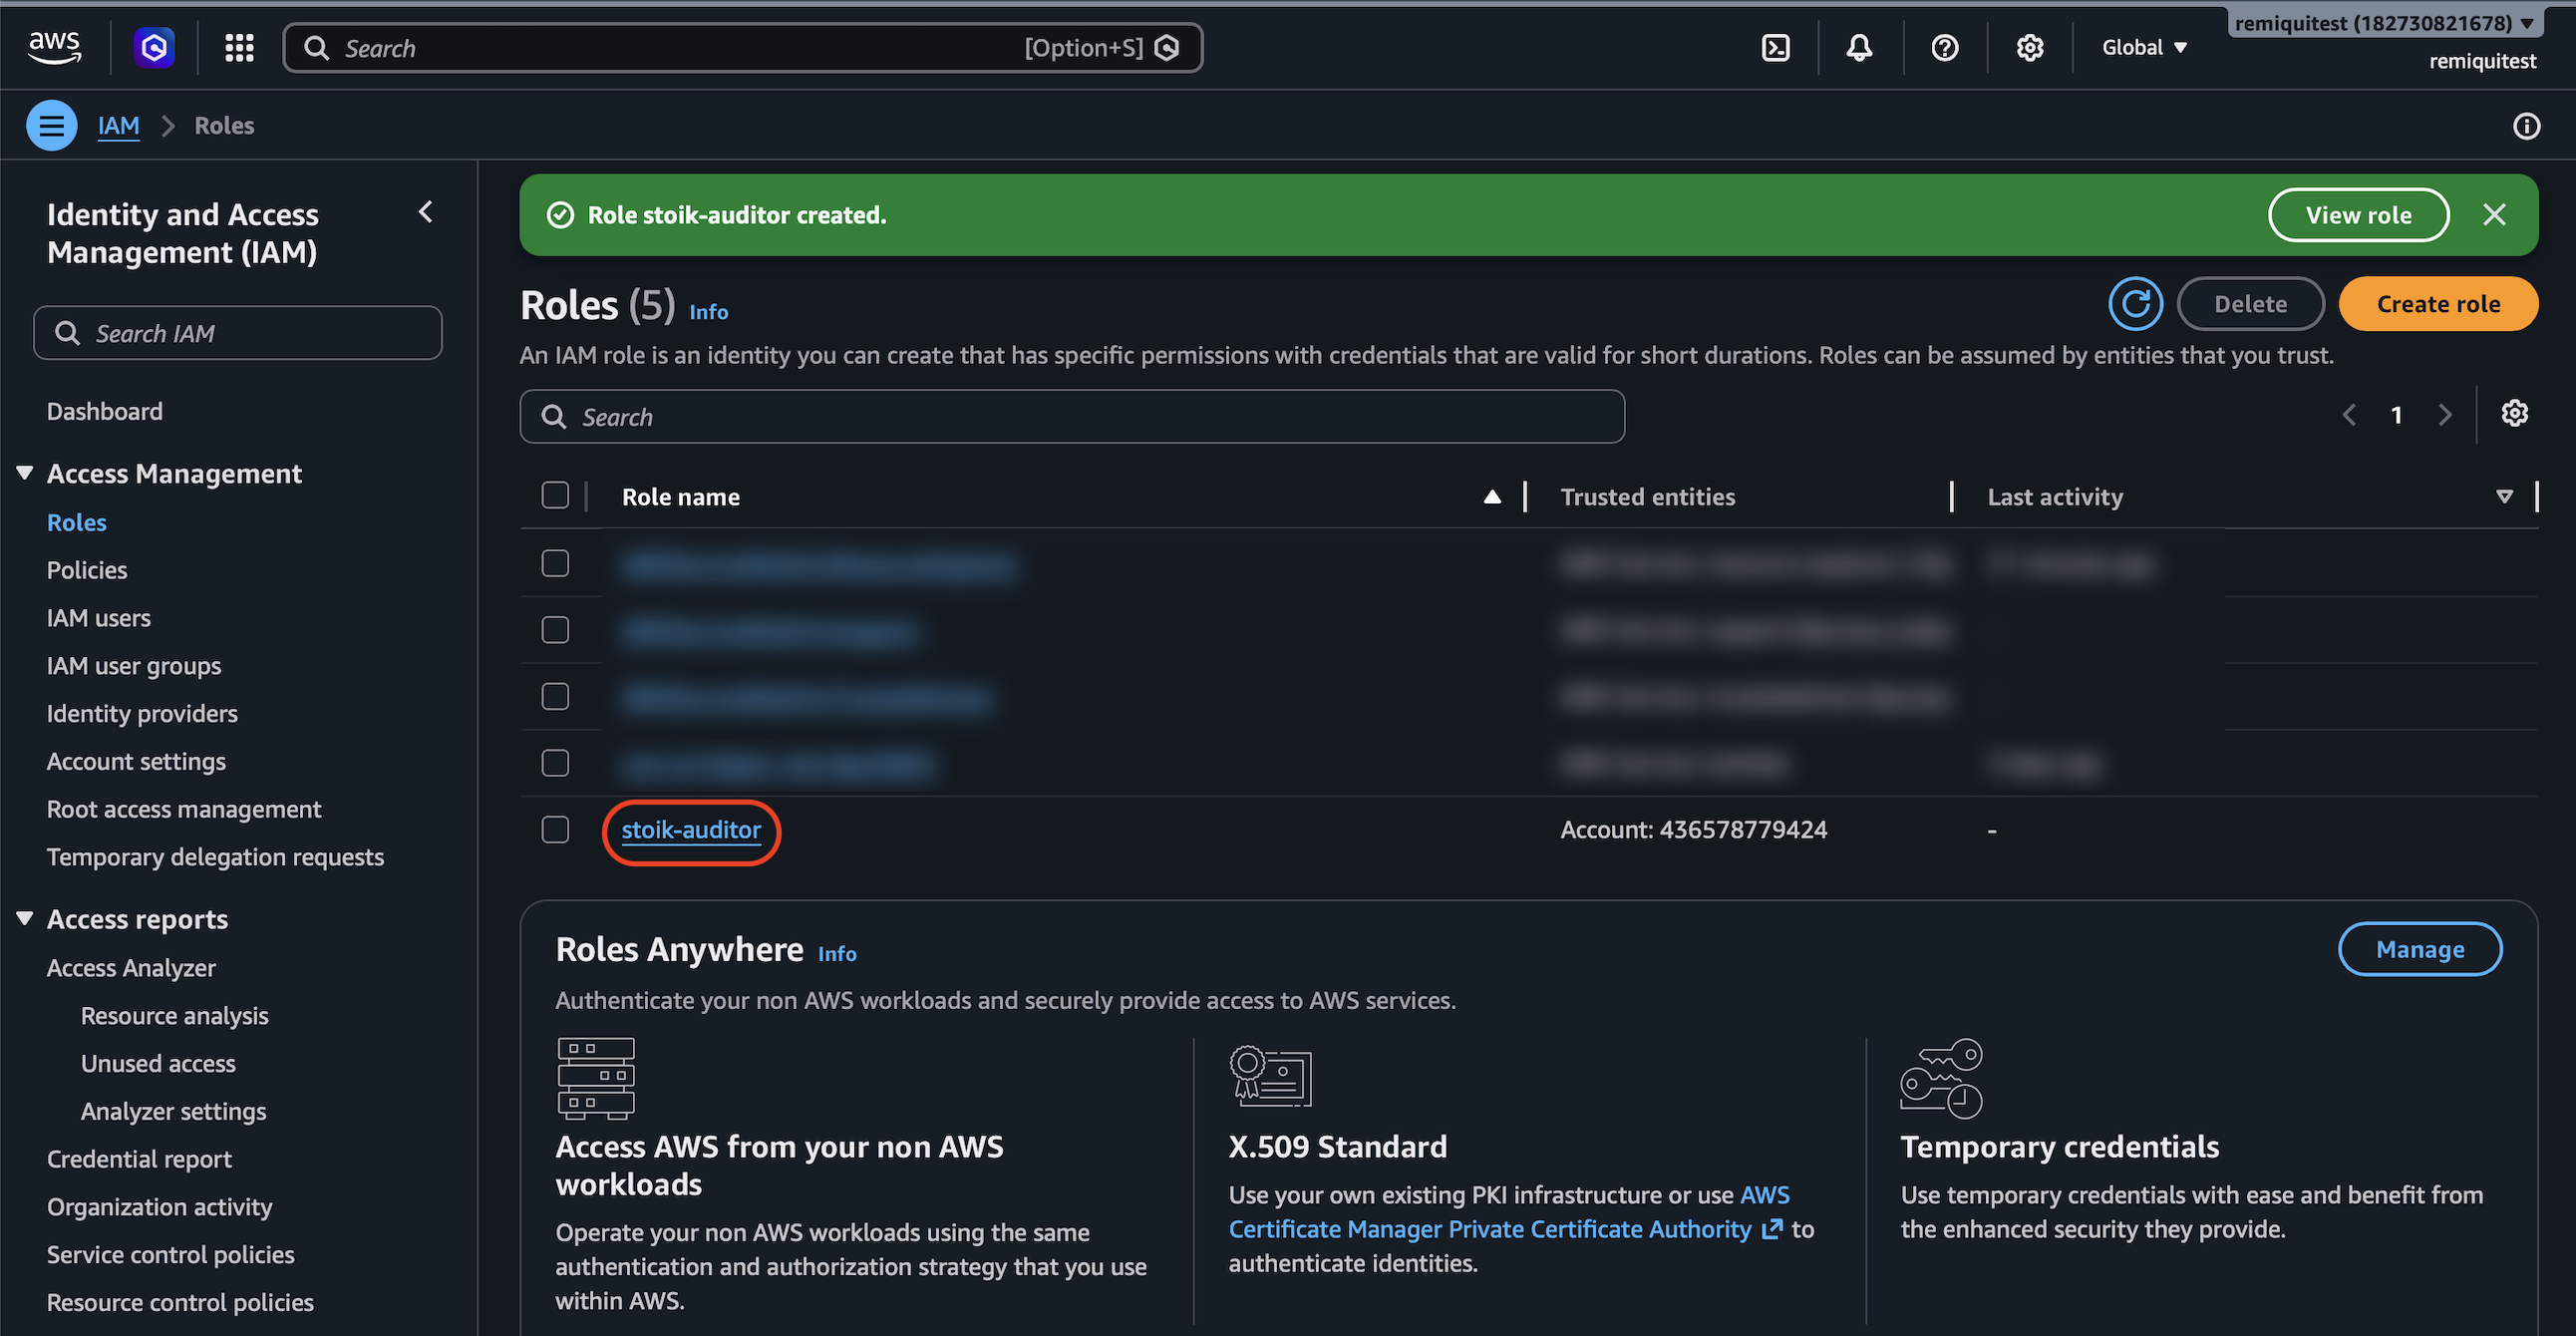
1. Go to the `stoik-auditor` role you just created.
2. Copy the `ARN` reference.
{% endstep %}
{% step %}
### Complete setup
1. Paste the `ARN` reference into the dedicated field in the Stoïk Protect console.
2. Click `Complete set-up`.
{% hint style="info" %}
Refresh the Stoïk Protect page if necessary.
{% endhint %}
{% endstep %}
{% endstepper %}
## AWS Organizations
With AWS Organizations, create the `stoik-auditor` role in each member account you want scanned, not only in the management account. All the permissions requested are read-only: the AWS-managed `SecurityAudit` policy plus `StoikAdditionalPermissions`. There is no smaller set.
## Troubleshooting
"Integration with AWS failed" / "Unable to assume role"
Check these in order, most common first:
1. **External ID:** the value in Stoïk Protect must match the `sts:ExternalId` in the role's trust policy exactly. Case and spaces count. An external ID from an earlier attempt fails too.
2. **Trusted account:** the trust policy trusts account `436578779424`.
3. **Role:** `stoik-auditor` exists in that account, and the ARN pasted in Stoïk Protect is its ARN. For a role that does not exist, AWS answers "access denied", not "not found".
4. **Policies:** both `SecurityAudit` and `StoikAdditionalPermissions` are attached, and the latter matches the JSON above. Older setups often miss `sso:Describe*` and `sso:List*`.
Everything is correct, but the setup still says "roles not correctly configured"
This is usually a Service Control Policy (SCP). Before accepting an account, Stoïk checks its role with AWS's permission simulator, and some SCPs make that simulator refuse every permission, even though the real scan works. Contact with your AWS account ID.
The scan worked, then stopped
Something changed on your side: the role was deleted or renamed, a policy was detached, the external ID changed, or a new SCP was added. Go through the four checks in ["Integration with AWS failed" / "Unable to assume role"](#integration-with-aws-failed--unable-to-assume-role).
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://docs.stoik.io/prevention-tools/cloud-scan/aws.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.