> For the complete documentation index, see [llms.txt](https://docs.stoik.io/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.stoik.io/prevention-tools/cloud-scan/gcp.md).
# Setup: GCP
Give the Cloud scan read-only access to a Google Cloud project by creating a service account that Stoïk can use.
## Prerequisites
* An administrator account is required to perform this deployment.
* A technical advisor is required for ongoing supervision and vulnerability remediation.
* One person does the whole setup, from start to finish: a Stoïk Protect user allowed to edit prevention tools, who is also an administrator of the GCP project.
## Setup
{% stepper %}
{% step %}
### Select Google Cloud Platform
Go to `Cloud Scan` > `Settings`, click `New Provider`, and select `Google Cloud Platform`.
{% endstep %}
{% step %}
### Open your Cloud Console
Go to the [Google Cloud Console](https://console.cloud.google.com/) and log in with your administrator account.
{% endstep %}
{% step %}
### Open the API library
Go to `APIs & Services` > `Library` in the left-hand menu.
{% endstep %}
{% step %}
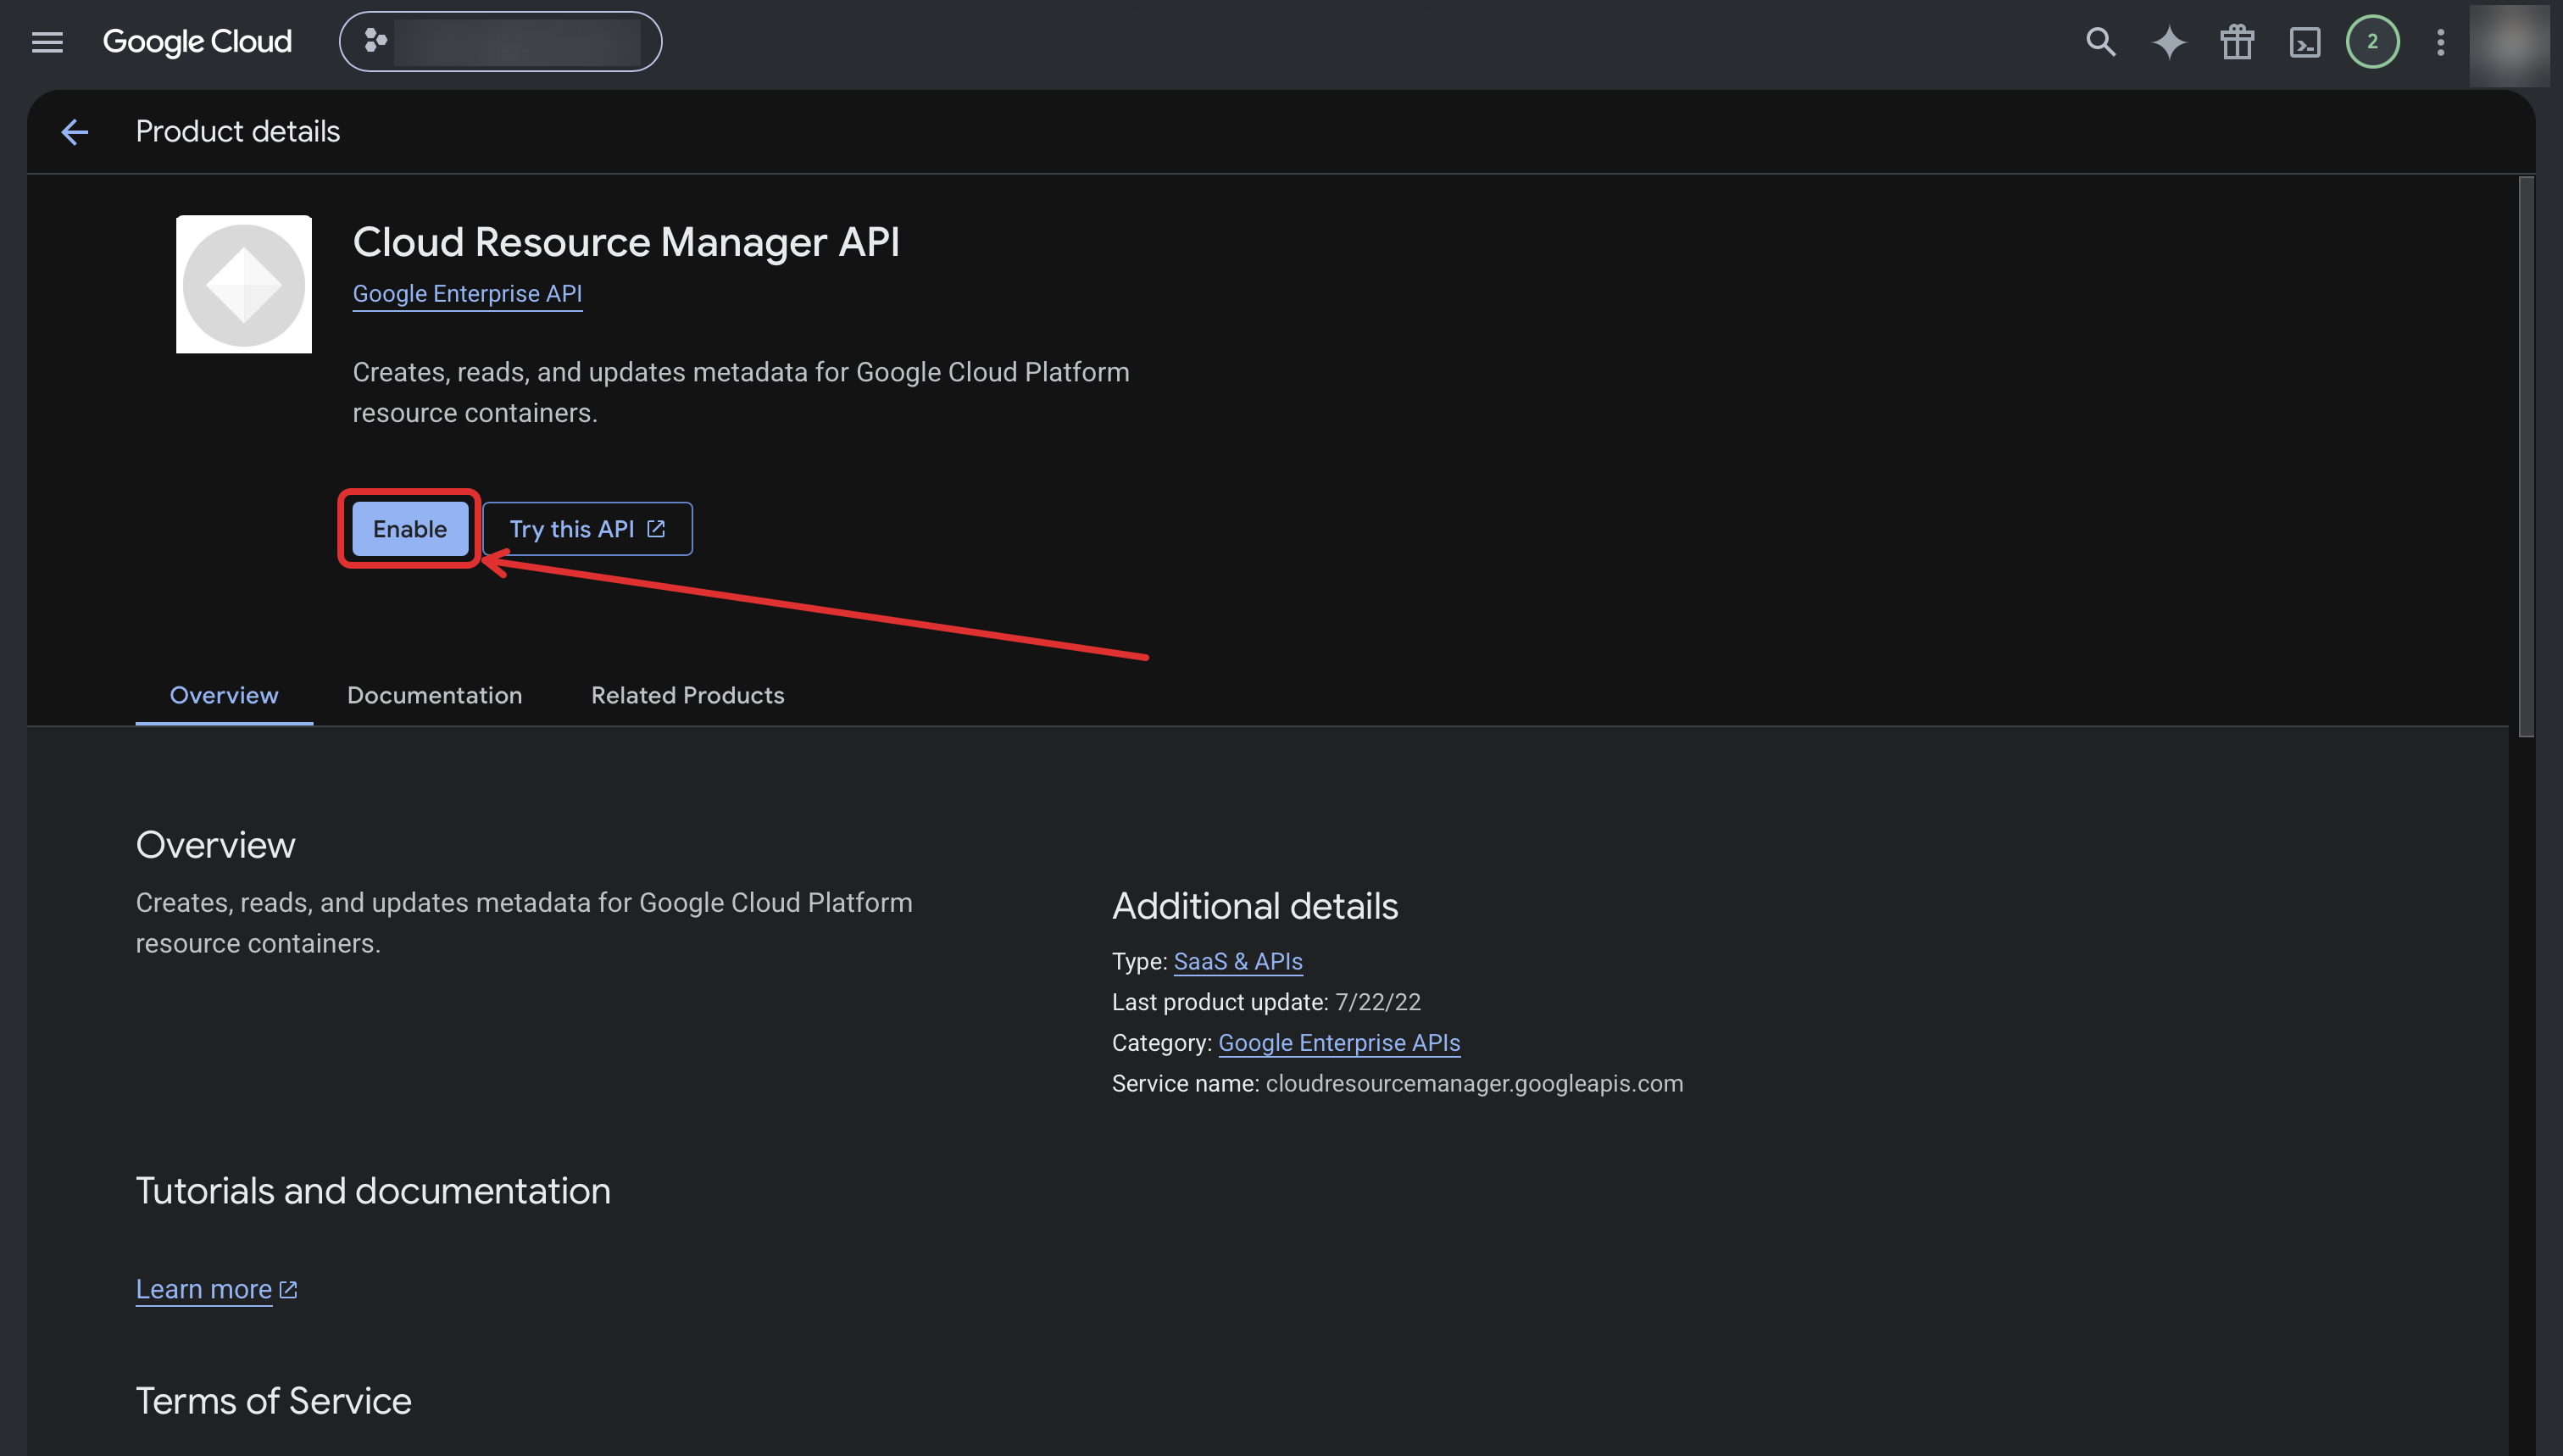
### Find the Cloud Resource Manager API
Search for `Cloud Resource Manager API` and click on it.
{% endstep %}
{% step %}
### Enable the API
Click `Enable`.
{% endstep %}
{% step %}
### Open the service accounts
Go to `IAM & Admin` > `Service Accounts` in the left-hand menu.
{% endstep %}
{% step %}
### Create the service account
Click `Create Service Account`.
{% endstep %}
{% step %}
### Name the service account
Enter `stoik-scanner` as the service account name, then click `Create and continue`.
{% endstep %}
{% step %}
### Assign roles
Add the following 3 roles: `Viewer`, `Security Reviewer`, `Stackdriver Accounts Viewer`.
Leave step 3 empty and click `Done`.
{% endstep %}
{% step %}
### Open the service account
Click on the service account you just created, then click `Principals with access`.
{% endstep %}
{% step %}
### Grant access
1. Select your service account and click `Grant access`.
2. Enter `stoik-scanner@stoik-gcp-scan-prod.iam.gserviceaccount.com` in the `New principals` field.
3. Assign the `Service Account Token Creator` role, then click `Save`.
{% endstep %}
{% step %}
### Copy the service account email
1. Click `Details` in GCP.
2. Copy the email address of the created service account.
{% endstep %}
{% step %}
### Complete setup
1. Paste the service account email address into the `Service Account Email` field in Stoïk Protect.
2. Click `Complete setup`.
{% hint style="info" %}
Refresh the Stoïk Protect page if necessary.
{% endhint %}
{% endstep %}
{% endstepper %}
## Projects to scan
Set up the projects that hold your servers and databases: a project created just for Stoïk is empty, so there is nothing to scan. The API must be enabled one project at a time.
## Troubleshooting
The setup failed, then worked when I retried
New roles, permissions and APIs take a few minutes to apply. Wait 5 minutes and click again.
"role/stackdriver.accounts.viewer must be assigned"
`Stackdriver Viewer` and `Stackdriver Accounts Viewer` are two different roles. The service account needs exactly `Viewer`, `Security Reviewer` and `Stackdriver Accounts Viewer`.
"do not belong to a permitted customer"
Your organization policy **Domain restricted sharing** (`iam.allowedPolicyMemberDomains`) blocks the Stoïk service account. Your admin adds Stoïk's customer ID `C01isw1kw` to the allowed values, in `IAM & Admin` > `Organization Policies`. This requires the `Organization Policy Administrator` role at the organization level: being Owner of the project is not enough.
"Integration with GCP failed" / getAccessToken denied
Two usual causes:
* The Cloud Resource Manager API is not enabled, or was enabled only a few minutes ago.
* `stoik-scanner@stoik-gcp-scan-prod.iam.gserviceaccount.com` did not get the `Service Account Token Creator` role on your service account.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://docs.stoik.io/prevention-tools/cloud-scan/gcp.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.